Operational Intelligencefor Critical Infrastructure
Cyber threats move fast. Decisions move slower.
Mithryl Systems transforms cybersecurity telemetry, operational data, engineering context, and human expertise into Operational Intelligence so organizations can protect operations, make better decisions, and Operate With Confidence.
 150+ Years
- of Combined OT and Critical Infrastructure Experience
 24×7×365
- OT Monitoring and Investigation
 Vendor Neutral
- Works with your existing tools and technology investments
 OT First
- Purpose built for industrial environments, protocols, and risk models
 Augmented Intelligence
- AI does the heavy lifting. Humans make the right calls.
 One Ecosystem
- Integrated capabilities working together for operational resilience
What is Operational Intelligence?
Operational Intelligence is the ability to transform cybersecurity telemetry, operational data, engineering context, and human expertise into actionable decisions that protect production, improve resilience, and reduce operational risk.
See What Matters
Converge IT and OT data with operational context to surface what truly matters.
Understand the Impact
Apply engineering and operational context to understand risk and impact.
Make Confident Decisions
Deliver prioritized insights with clear options for safe, effective action.
Strengthen Operations
Improve resilience, reduce downtime, and protect what powers the world.
Why OT Cybersecurity is Different
- Availability and safety come before confidentiality.
- Systems cannot be patched or rebooted like IT.
- Downtime impacts people, production, and the economy.
- Engineering context is required to make the right call.
- Decisions in OT must be safe, coordinated, and precise.
An Alert Doesn’t Tell You What To Do
1. Alert
Engineering workstation generated unexpected behavior.
2. Decision Point
Isolate the asset?
3A. If Yes
Production stops. Operations are impacted.
3B. If No
Adversary could reach controllers. Risk spreads.
The Answer
Operational Intelligence provides the context you need.
Better decisions require more than alerts. They require Operational Intelligence.
What is OT MDR?
Mithryl Systems OT MDR is a 24×7 managed cybersecurity service that combines advanced detection, deep OT expertise, and Augmented Intelligence to detect threats earlier, investigate faster, and guide safe, effective response.
How It Works
1. Observe
Collect telemetry across IT and OT.
2. Correlate
Apply Augmented Intelligence and detect threats.
3. Investigate
Add operational context and human expertise.
4. Understand
Assess impact to operations.
5. Recommend
Guide safe and effective response.
6. Improve
Continuously tune detections and outcomes.
One Ecosystem. Complete Operational Intelligence.
Integrated capabilities working together to protect what matters most.
Unlike point solutions, Mithryl Systems delivers an integrated Operational Intelligence ecosystem where every capability continuously strengthens the others.
Explore all capabilitiesExecutive Outcomes
- Reduce operational risk and prevent disruptive events
- Protect production, people, and critical assets
- Accelerate decisions with operational clarity
- Improve resilience and maintain continuity
- Strengthen compliance and audit confidence
- Maximize existing technology investments
Purpose Built for OT. Ready for What’s Next.
24×7×365
Always on expert coverage.
Purdue Aware
Safety first, operationally safe.
Augmented Intelligence
Human and AI working together.
Tool Agnostic
Integrates with your investments.
Proven Impact
Measurable business value.
Operational Context
Understands what cyber risk means to operations.
Resources & Insights
Showing 7 of 7 resources.
Article
When Modbus Lies: Detecting Threats Inside Industrial Protocols
Read article
Article
When Playbook Meets Adversary
Read article
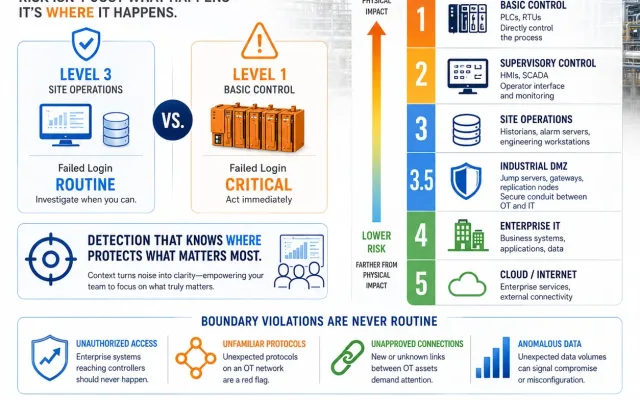
Article
Same Alert, Different Impact
Read article
Article
OT IR as Operational Discipline
Read article
Article
The Leadership Layer, Part 9: Deciding Under Pressure
Read article
Podcast
Energy Systems: Real Threats. Real Consequences
Listen now
Webinar
Turning Compliance Into Operational Readiness
Watch now
Frequently Asked Questions
What is Operational Intelligence for Critical Infrastructure?
Operational Intelligence is Mithryl Systems' approach to helping organizations make better operational cybersecurity decisions. It combines cybersecurity telemetry, operational context, engineering expertise, and augmented intelligence to help organizations reduce operational risk, improve resilience, and protect production.
Unlike traditional cybersecurity programs that focus primarily on detecting threats, Operational Intelligence focuses on understanding operational impact. Every alert is evaluated in the context of safety, reliability, production, regulatory obligations, and business risk so organizations can make informed decisions without disrupting operations.
What is OT Managed Detection & Response (OT MDR)?
OT Managed Detection & Response (OT MDR) is a 24x7 managed cybersecurity service designed specifically for Operational Technology (OT) environments. Mithryl Systems continuously monitors industrial systems, investigates threats using operational context, performs proactive threat hunting, improves detection quality, and provides expert guidance during cybersecurity incidents.
OT MDR is delivered by experienced OT cybersecurity professionals who understand industrial protocols, engineering processes, and critical infrastructure operations.
How is OT MDR different from traditional Managed Detection & Response?
Traditional MDR services were built for enterprise IT environments where protecting data is the primary objective.
OT MDR is designed for industrial environments where protecting people, production, reliability, and operational continuity are equally important.
Mithryl Systems combines industrial engineering expertise, OT-specific detection engineering, operational context, and augmented intelligence to provide recommendations that support safe operations instead of simply blocking threats.
Why is Operational Technology (OT) cybersecurity different from IT cybersecurity?
Operational Technology controls physical processes such as power generation, manufacturing, water treatment, pipelines, transportation, and industrial automation.
Unlike IT systems, OT environments often cannot tolerate downtime, automated isolation, or aggressive security controls that interrupt production.
Effective OT cybersecurity requires understanding operational processes, engineering constraints, safety implications, and business impact before taking action.
What is OT Cyber Fusion?
OT Cyber Fusion is Mithryl Systems' operational model for bringing together cybersecurity, operational technology, engineering, governance, business leadership, and operational risk into a single decision-making framework.
Instead of operating in disconnected silos, Cyber Fusion enables organizations to share information across teams, improve visibility, prioritize operational risk, and make faster, more informed decisions.
It creates alignment between IT security teams, OT operations, engineering, compliance, and executive leadership.
What does Operational Intelligence actually do?
Operational Intelligence helps organizations answer questions that security tools alone cannot answer.
For example:
- Which cyber event creates the greatest operational risk?
- Should this asset be isolated or monitored?
- What production processes could be affected?
- What regulatory obligations exist?
- What operational response is safest?
Rather than simply generating alerts, Operational Intelligence provides context that supports confident decision making.
Does Mithryl Systems replace our existing cybersecurity tools?
No.
Mithryl Systems is vendor neutral and is designed to work alongside your existing cybersecurity investments.
Our services integrate with SIEMs, EDR platforms, XDR platforms, OT monitoring solutions, firewalls, vulnerability management platforms, and industrial cybersecurity technologies to improve visibility, detection quality, investigations, and operational decision making without requiring organizations to replace existing tools.
What is Augmented Intelligence and how does Mithryl use it?
Augmented Intelligence uses artificial intelligence to improve the speed and quality of human decision making rather than replacing human expertise.
Mithryl Systems uses Augmented Intelligence to correlate telemetry, identify meaningful patterns, improve threat prioritization, enhance investigations, recommend detection improvements, and surface operational context.
Experienced OT analysts always validate findings before operational recommendations are made.
What industries benefit from Operational Intelligence?
Operational Intelligence is valuable for any organization operating critical infrastructure or industrial systems.
Common industries include:
- Electric Utilities
- Renewable Energy
- Oil and Gas
- Water and Wastewater
- Manufacturing
- Transportation
- Critical Manufacturing
- Industrial Facilities
The Operational Intelligence model is designed around operational complexity rather than a specific industry.
How long does it take to deploy OT MDR?
Deployment timelines depend on the size and complexity of the environment.
Organizations with existing OT visibility platforms can often begin receiving monitoring and investigation services within weeks. Additional capabilities such as Detection Engineering, Cyber Fusion Strategy, and Operational Intelligence reporting are typically introduced in phases to maximize long-term value.
Can Mithryl Systems integrate with Dragos, Claroty, Nozomi, Armis, or Microsoft?
Yes.
Mithryl Systems integrates with many leading OT and IT cybersecurity platforms, including solutions such as Dragos, Claroty, Nozomi Networks, Armis, Microsoft Sentinel, Microsoft Defender, Splunk, Palo Alto Networks, CrowdStrike, and other technologies.
Our approach is vendor neutral and designed to maximize the value of existing technology investments.
Does Mithryl Systems support NERC CIP, IEC 62443, and other cybersecurity regulations?
Yes.
Mithryl Systems helps organizations improve operational resilience while supporting cybersecurity frameworks and regulatory requirements, including:
- IEC 62443
- NERC CIP
- NIST Cybersecurity Framework
- NIST SP 800-82
- TSA Security Directives
- NIS2
- Sector-specific compliance requirements
Our services align cybersecurity operations with governance, reporting, and executive oversight.
How does Mithryl Systems improve operational resilience?
Operational resilience improves when organizations can detect threats earlier, understand operational impact faster, and respond with confidence.
Mithryl Systems strengthens resilience by improving visibility, reducing detection blind spots, engineering higher-quality detections, providing expert investigations, and helping organizations make operationally informed decisions throughout the cybersecurity lifecycle.
What makes Mithryl Systems different from other OT cybersecurity providers?
Mithryl Systems is built around Operational Intelligence rather than individual cybersecurity products.
Our approach combines:
- OT cybersecurity expertise
- Industrial engineering knowledge
- Detection Engineering
- Digital Forensics
- Incident Response
- OT Cyber Fusion Strategy
- Augmented Intelligence
- Executive governance
- Continuous operational improvement
Rather than delivering isolated cybersecurity services, Mithryl Systems helps organizations build a continuously improving Operational Intelligence capability.
How do I get started with Mithryl Systems?
Most organizations begin with an Operational Intelligence Assessment.
During this engagement, Mithryl Systems evaluates your operational environment, cybersecurity capabilities, visibility gaps, operational risks, existing technologies, and business priorities.
The outcome is a prioritized roadmap that helps strengthen operational resilience, improve detection quality, reduce cyber risk, and align cybersecurity investments with business objectives.
Ready to Operate With Confidence?
See how Mithryl Systems transforms cybersecurity data into Operational Intelligence.