Resources
Articles from theoperational front line.
The article archive collects every article from the practice: OT security, detection, incident response and the operational realities of defending industrial environments.
All articles
Topic
Year
Showing 121 of 121 articles.
- OT & ICS
Mithryl Systems Launches Flagship OT Managed Detection & Response Service
Mithryl Systems, the DBA of PhishCloud, Inc., launches purpose-built OT MDR with 24x7x365 monitoring, detection engineering, and Operational Intelligence for critical infrastructure.
Detection & Monitoring · Risk & Leadership
 Detection & Monitoring
When Modbus Lies: Detecting Threats Inside Industrial Protocols
FrostyGoop used valid Modbus commands to disrupt heating in Ukraine. The attack shows why OT detection must understand industrial protocol intent and operational context.
 Detection & Monitoring
When Playbook Meets Adversary
A CISA red team operated undetected for three months inside a mature critical infrastructure environment and surfaced thirteen missed detections.
Incident Response · Ransomware · Governance & Compliance · Threat Intelligence
 OT & ICS
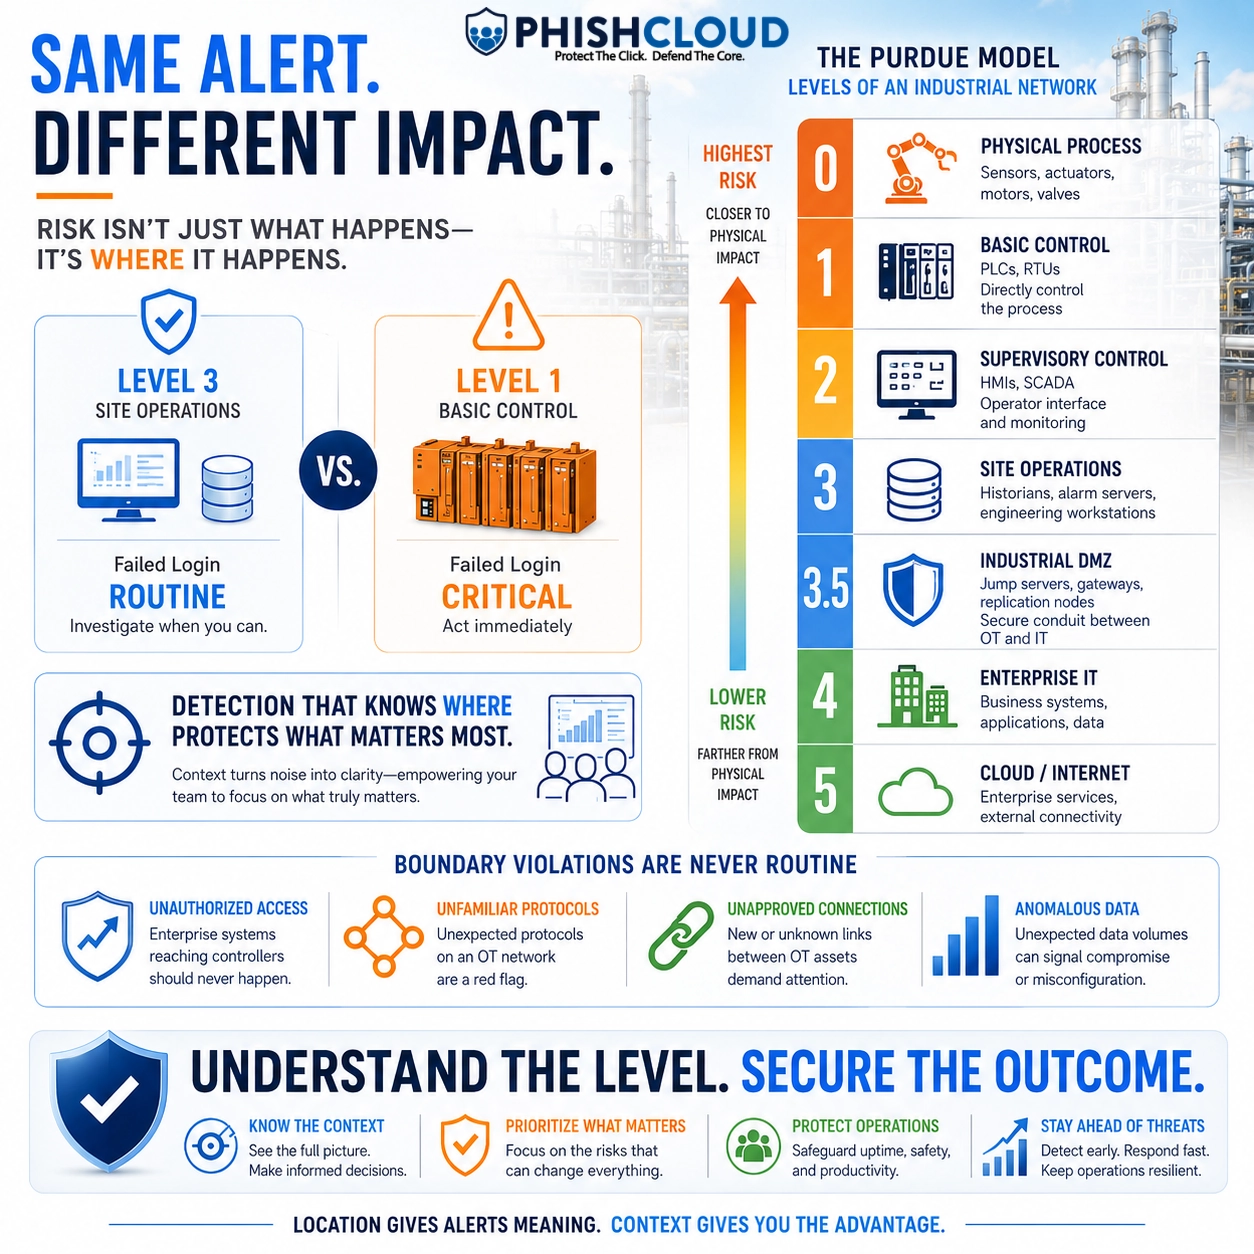
Same Alert, Different Impact
A failed login can be routine at Level 3 and crisis-level at Level 1. That is the hidden flaw in flat OT detection logic inherited from IT.
Detection & Monitoring
 Detection & Monitoring
OT IR as Operational Discipline
OT teams keep incident response plans on paper, but real incidents expose the gap between documentation and disciplined execution. When safety, uptime, and engineering decisions collide, untested playbooks break fast.
Incident Response · Ransomware · Risk & Leadership
 OT & ICS
Shared Attack Paths
Most detection teams map only MITRE ATT&CK for Enterprise, then miss the pivot that matters most.
Detection & Monitoring · Ransomware
 Incident Response
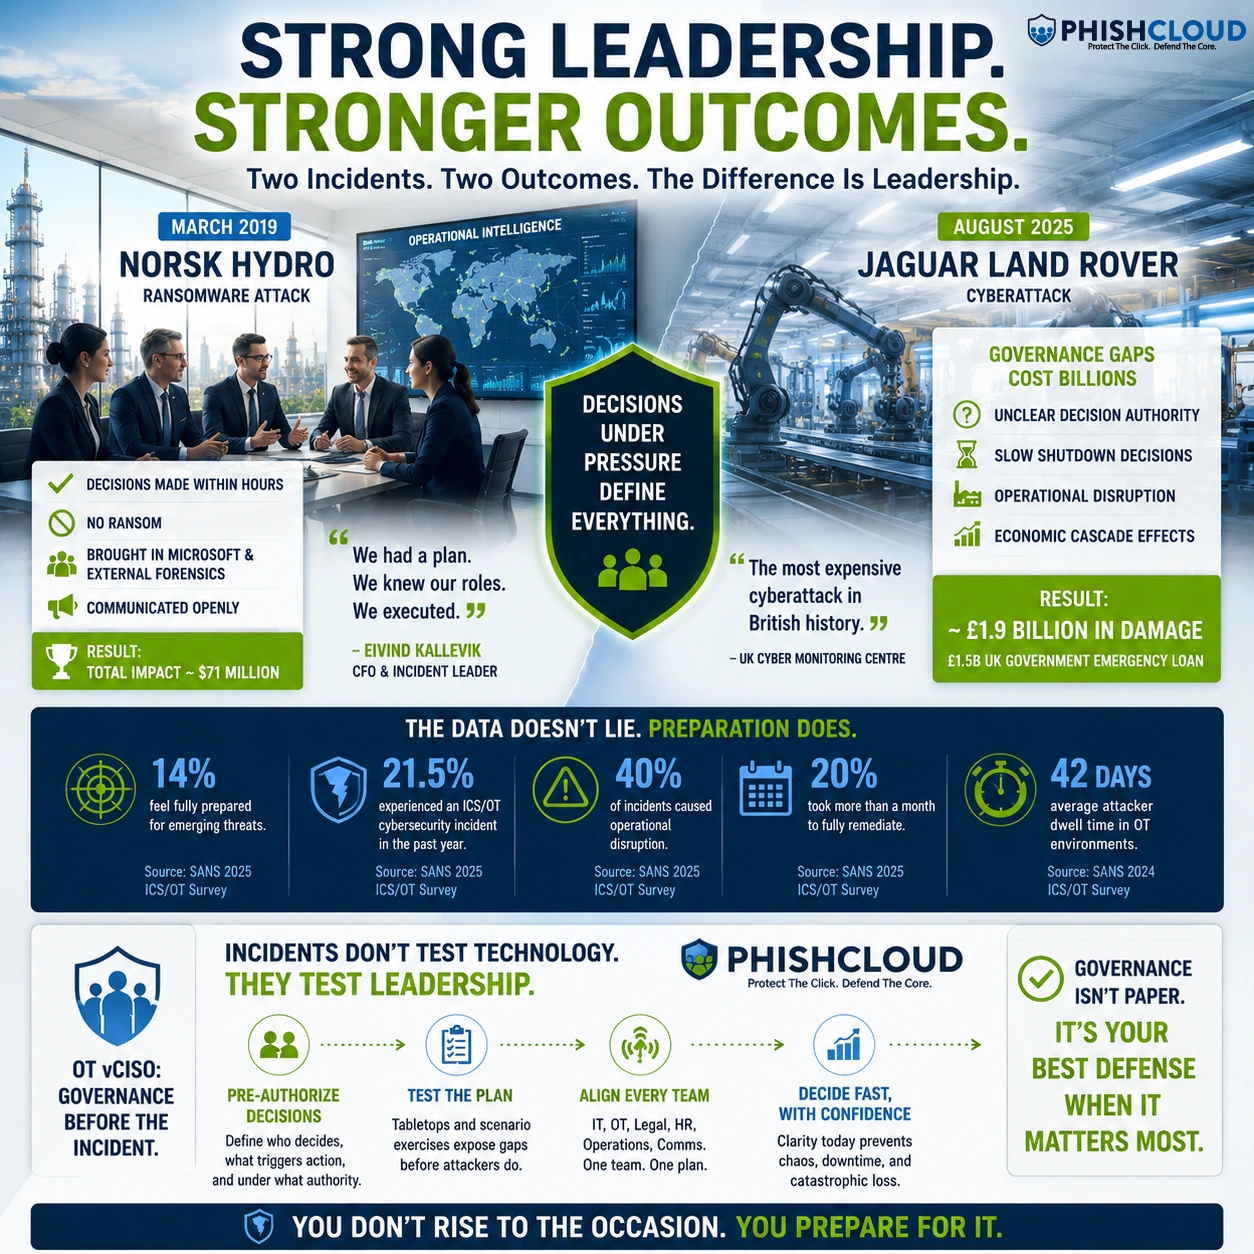
The Leadership Layer, Part 9: Deciding Under Pressure
Only 14% of industrial teams say they are fully prepared for emerging threats, yet incidents keep crossing from cyber disruption into operational shutdown.
Ransomware · Governance & Compliance · Risk & Leadership
 Detection & Monitoring
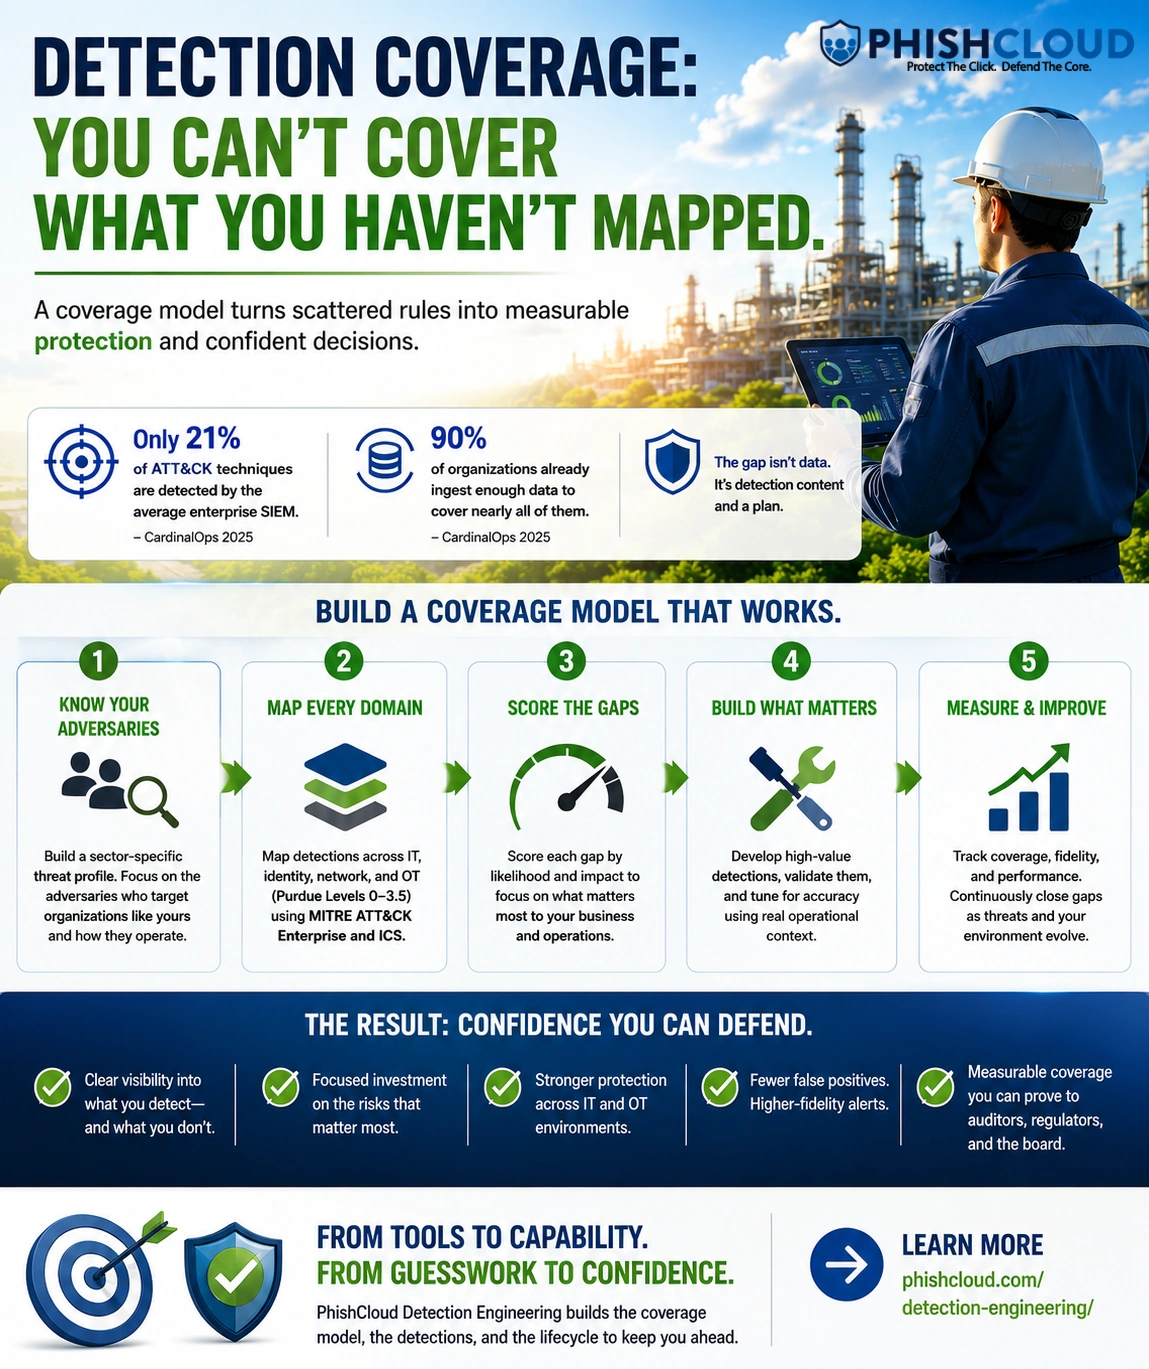
Detection Coverage: You Can't Protect What You Don't Know
CardinalOps found most teams detect only 19% of mapped ATT&CK behavior while 87% coverage is possible with data they collect. That gap is where attacks move from IT footholds into operational impact.
Threat Intelligence
 Detection & Monitoring
The Compliance Trap: What the Red Team Finds That Audits Miss
CISA's SILENTSHIELD Red Team operated inside a federal civilian agency's network for five months before anyone in the organization knew.
Incident Response · Governance & Compliance · Threat Intelligence
 OT & ICS
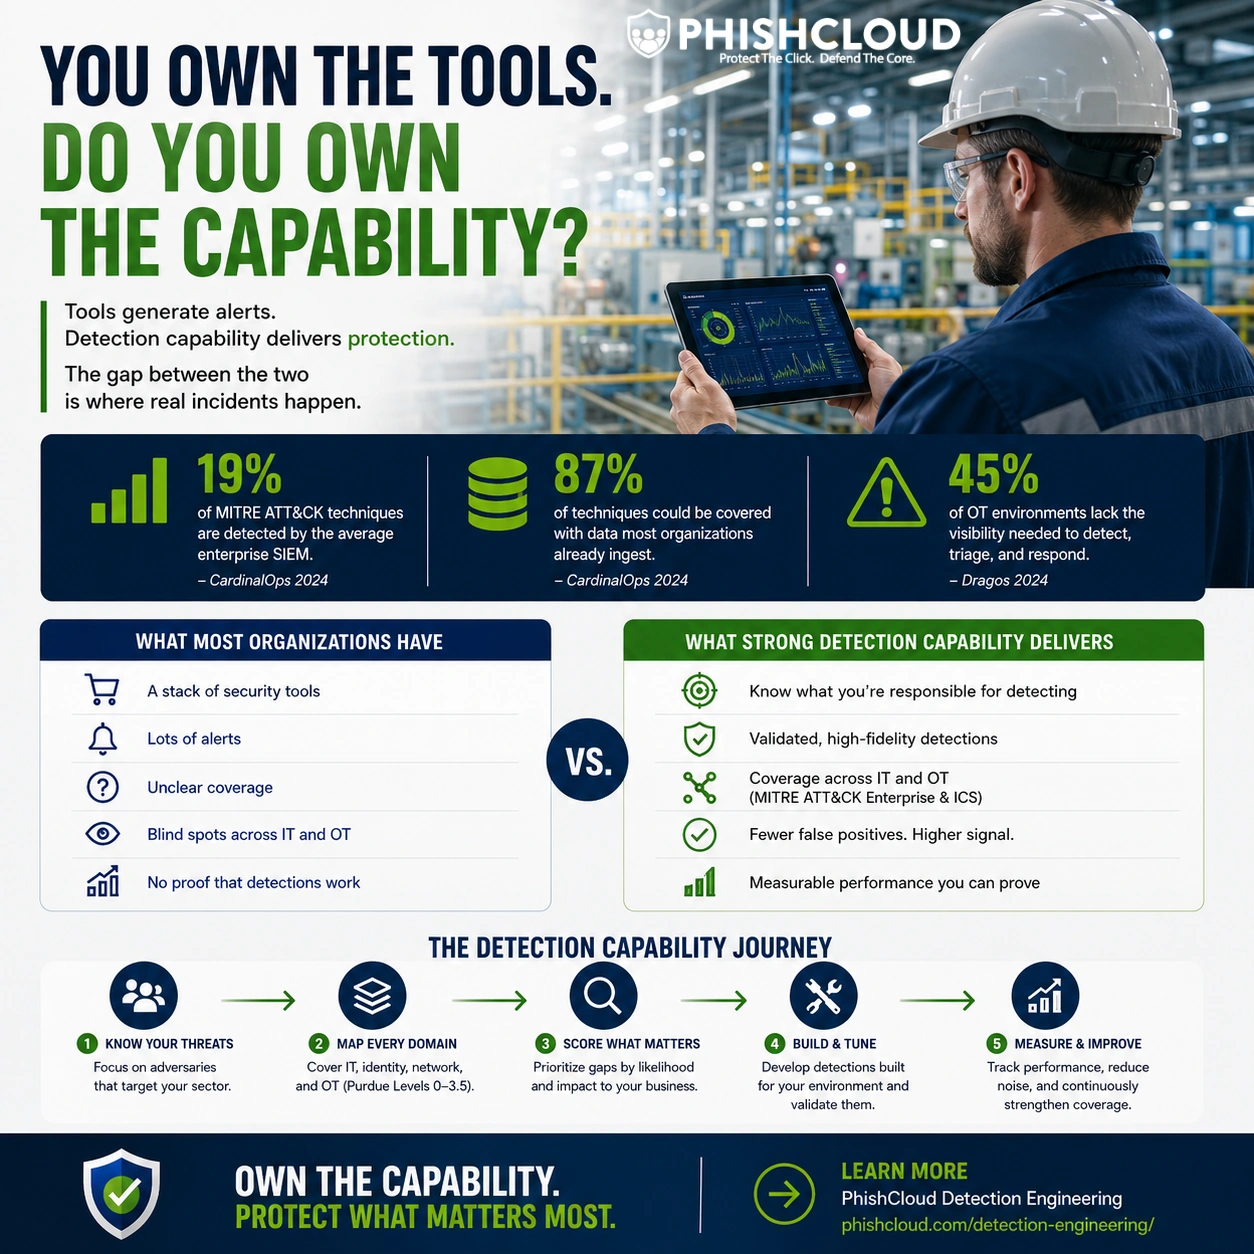
You Own the Detection Tools. Do You Own the Capability?
You bought the SIEM, deployed EDR, and added OT monitoring, but one question still stalls the room: what do your tools actually detect tonight?
Detection & Monitoring
 Detection & Monitoring
The Compliance Trap: What the Red Team Finds That Audits Miss
Five months undetected in a compliance-audited federal network was not a theoretical failure. CISA’s SILENTSHIELD proved how documented controls can coexist with full domain compromise and partner-lateral movement.
Incident Response · Governance & Compliance · Threat Intelligence
 Detection & Monitoring
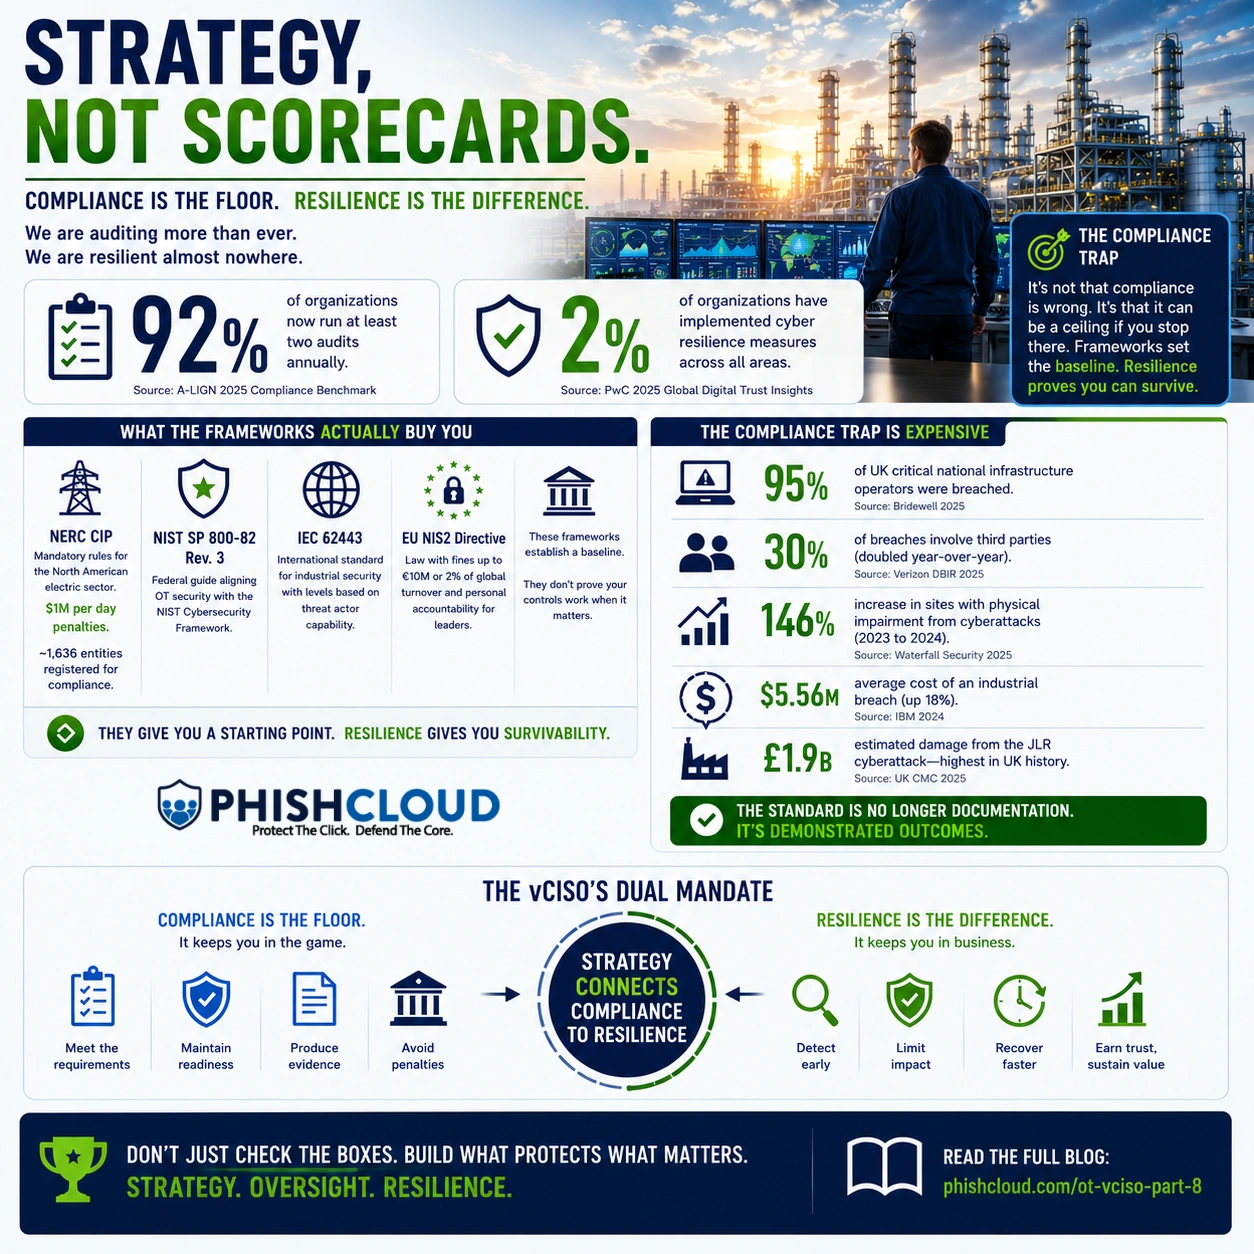
Strategy, Not Scorecards
Only 2% of organizations have cyber resilience across critical areas, yet 92% now run multiple audits every year. That gap is the OT compliance trap: documents pass while operations remain exposed. From JLR's £1.
Incident Response · Governance & Compliance · Risk & Leadership
 Detection & Monitoring
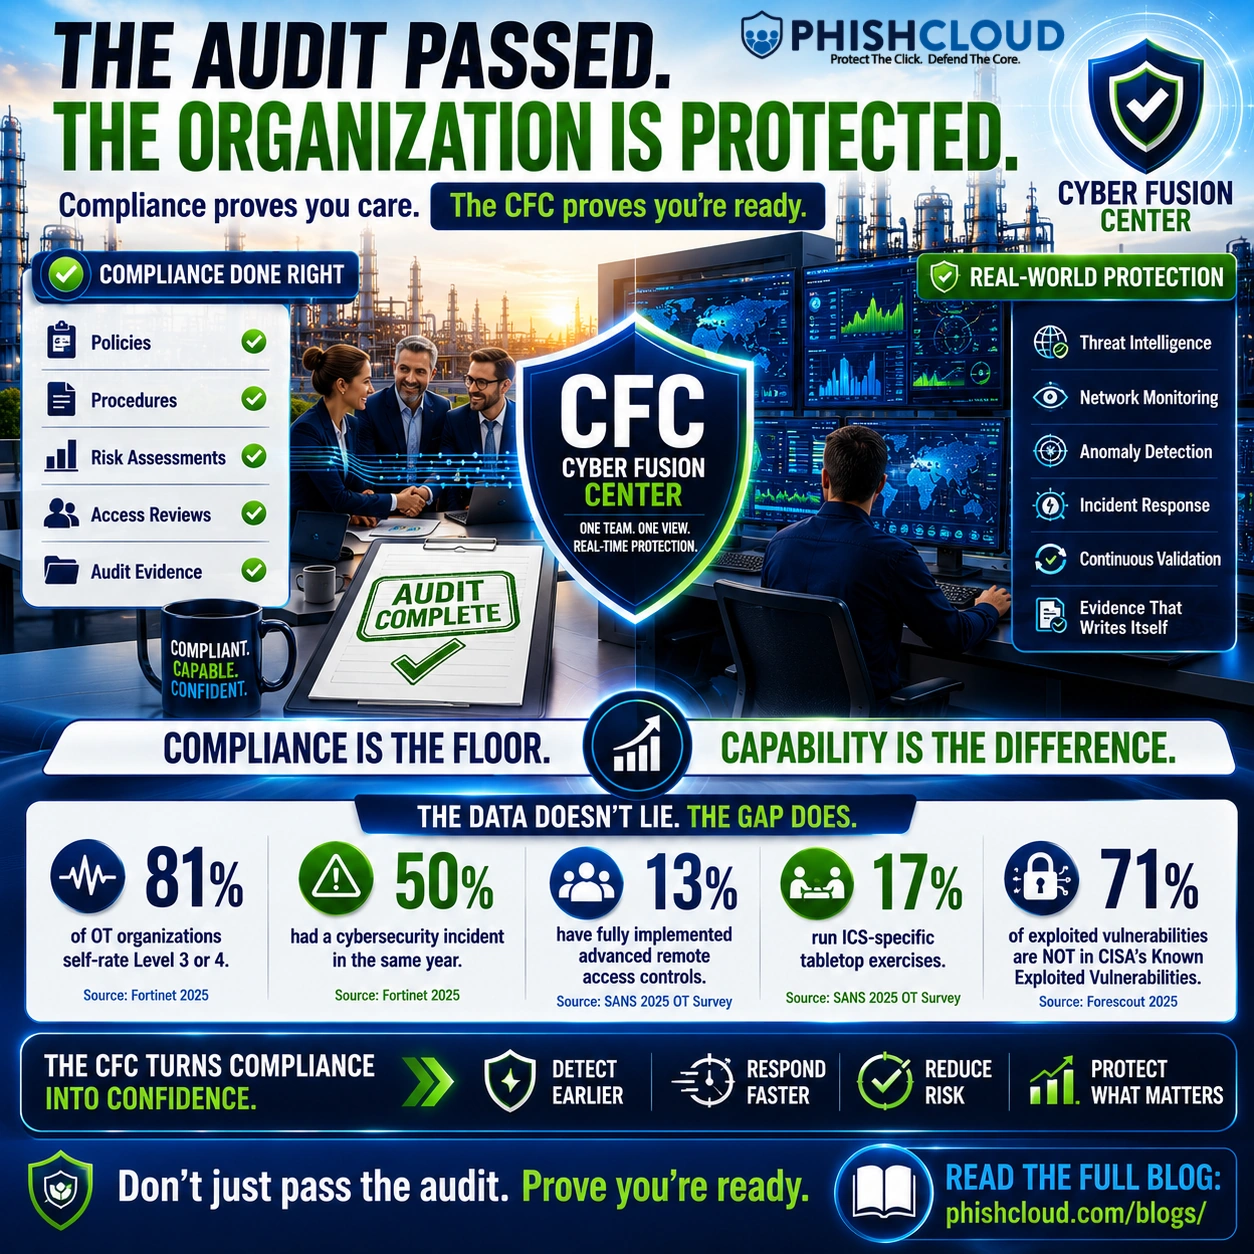
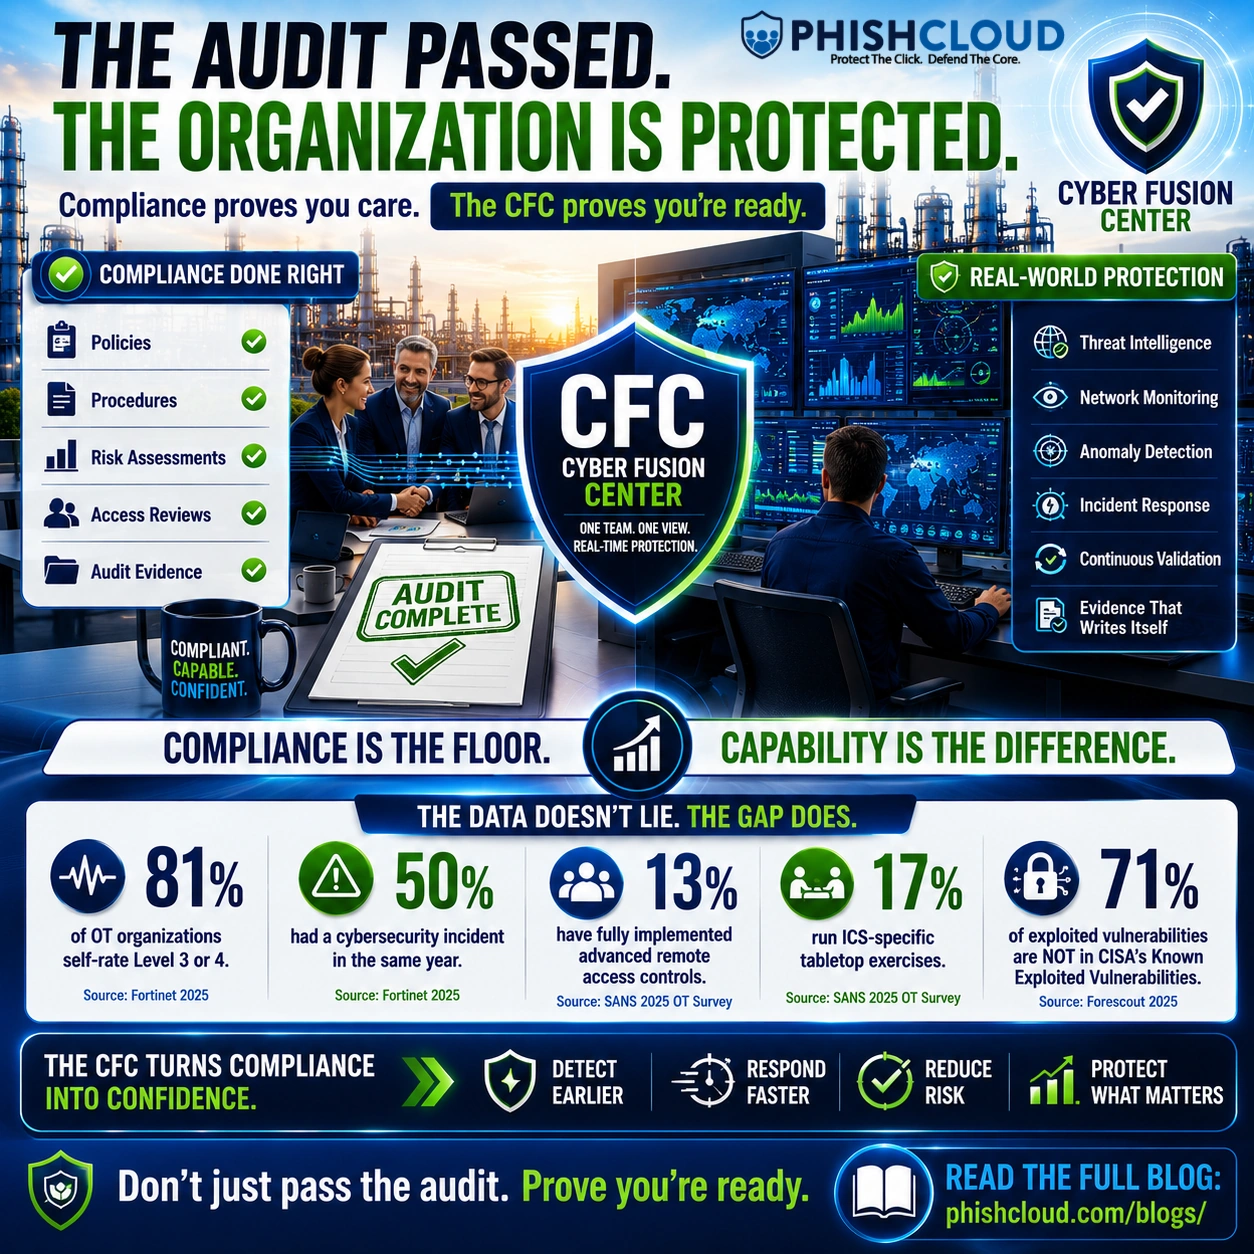
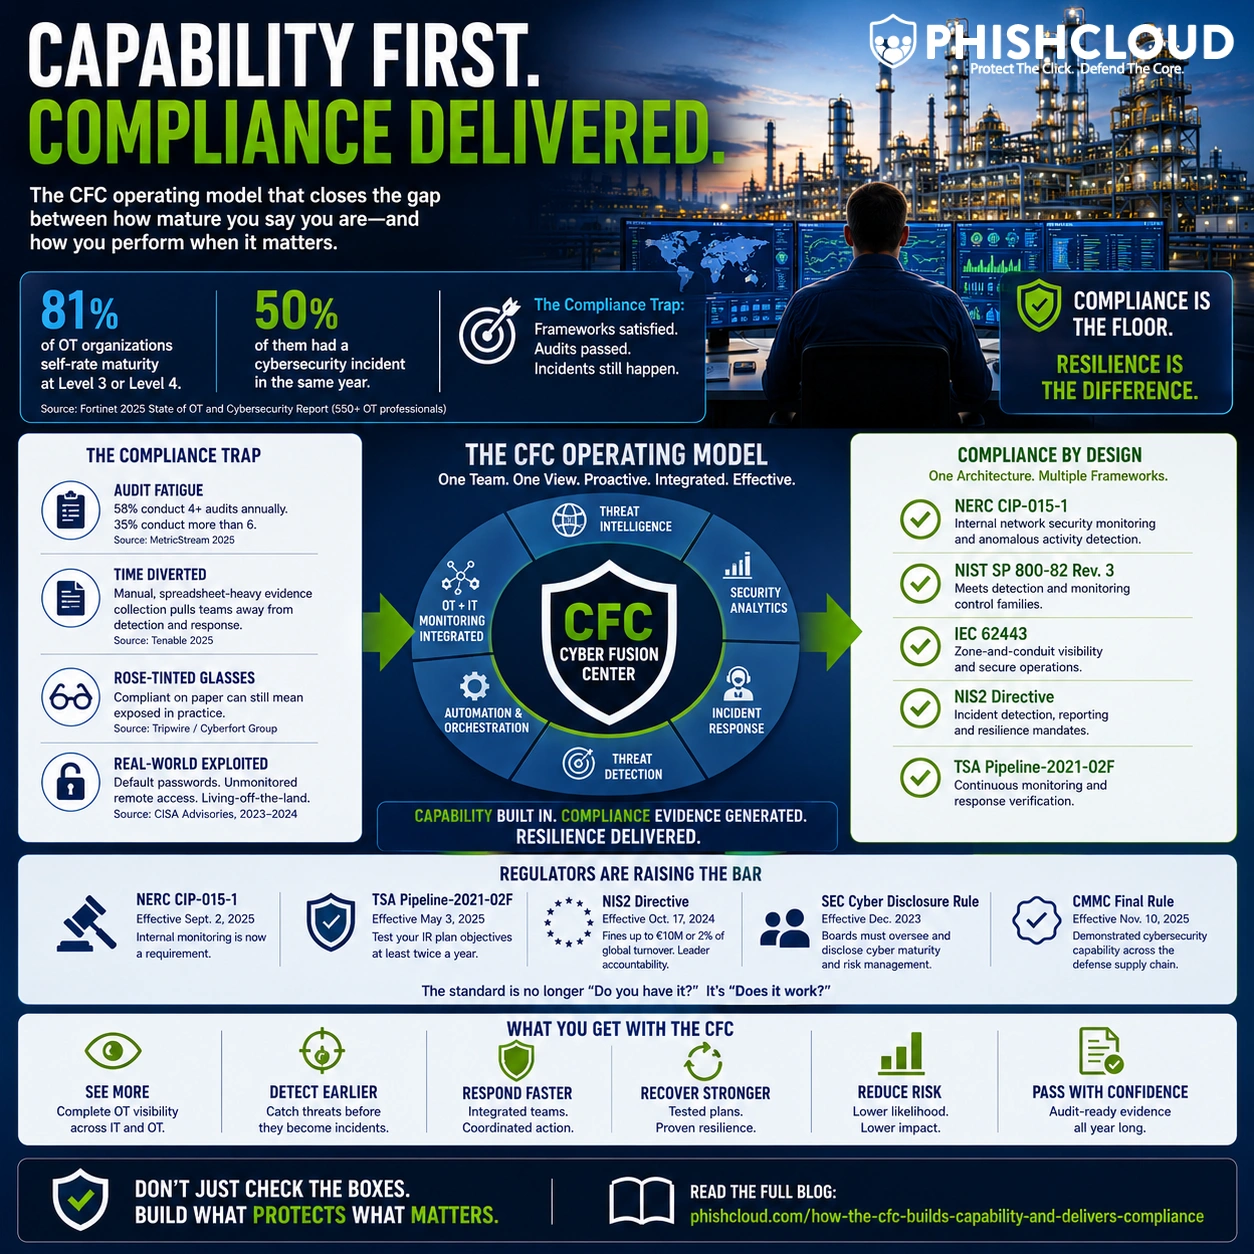
How the CFC Builds Capability and Delivers Compliance
Eighty-one percent of OT organizations now self-rate cybersecurity maturity at Level 3 or Level 4. Half reported a cybersecurity incident in the same year,
Incident Response · Governance & Compliance · Threat Intelligence
 Detection & Monitoring
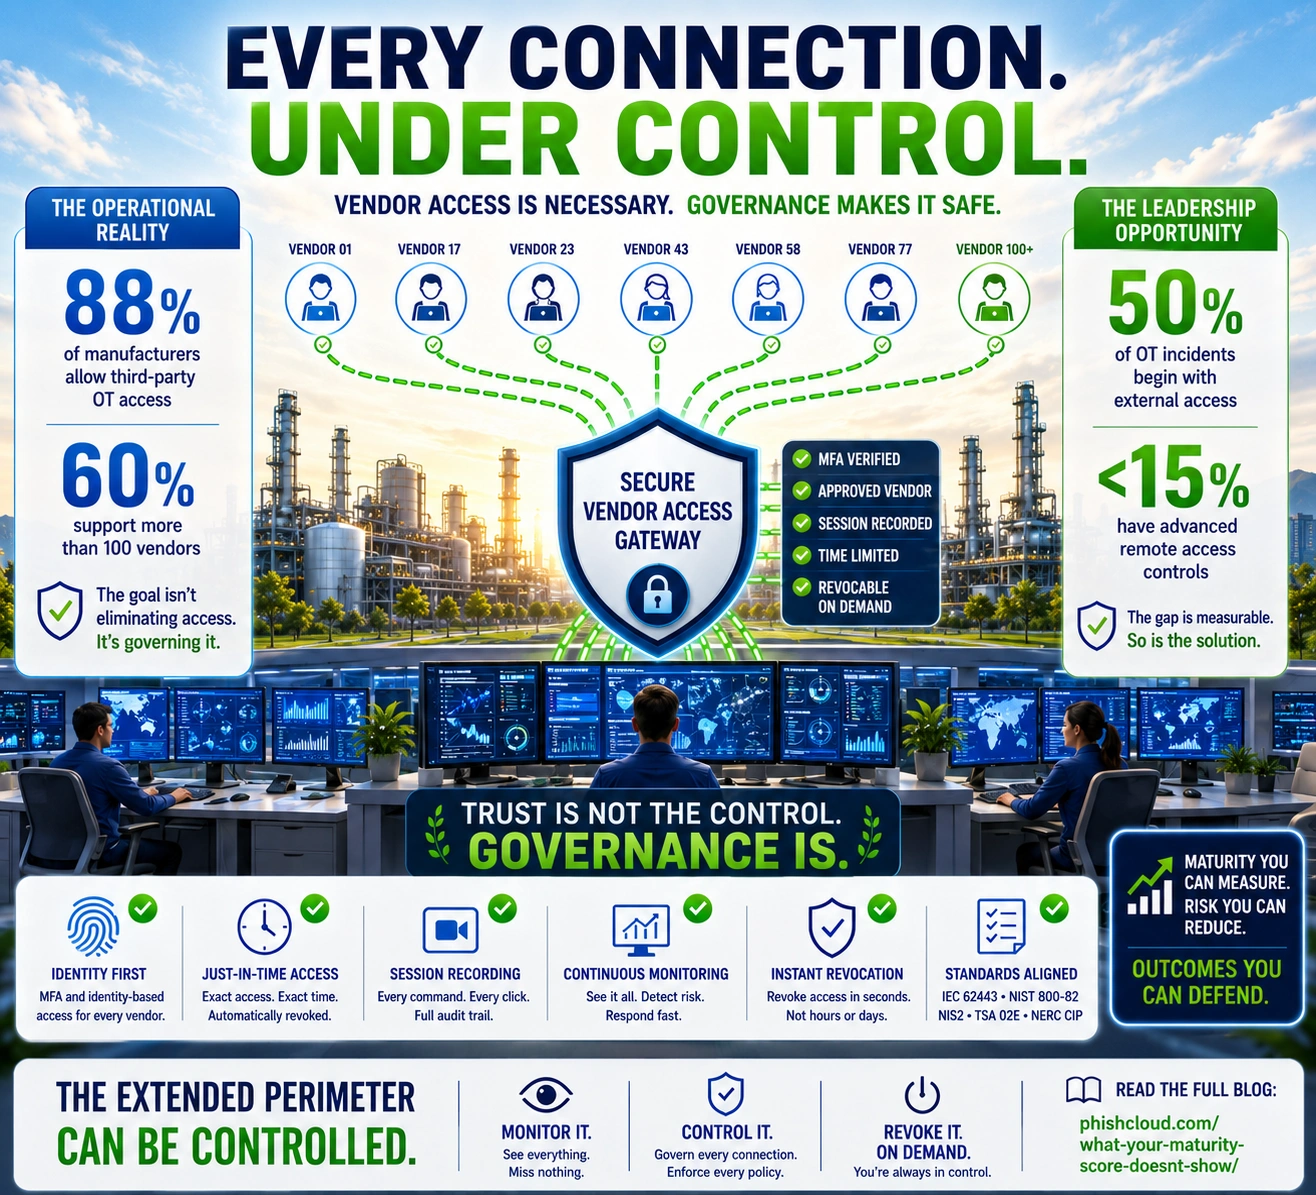
How the Red Team Walks In Through the Front Door of OT
Attackers crippled Polish energy sites in 2025 using default credentials and vendor pathways that should have been closed years earlier.
Incident Response · Ransomware · Governance & Compliance
 Detection & Monitoring
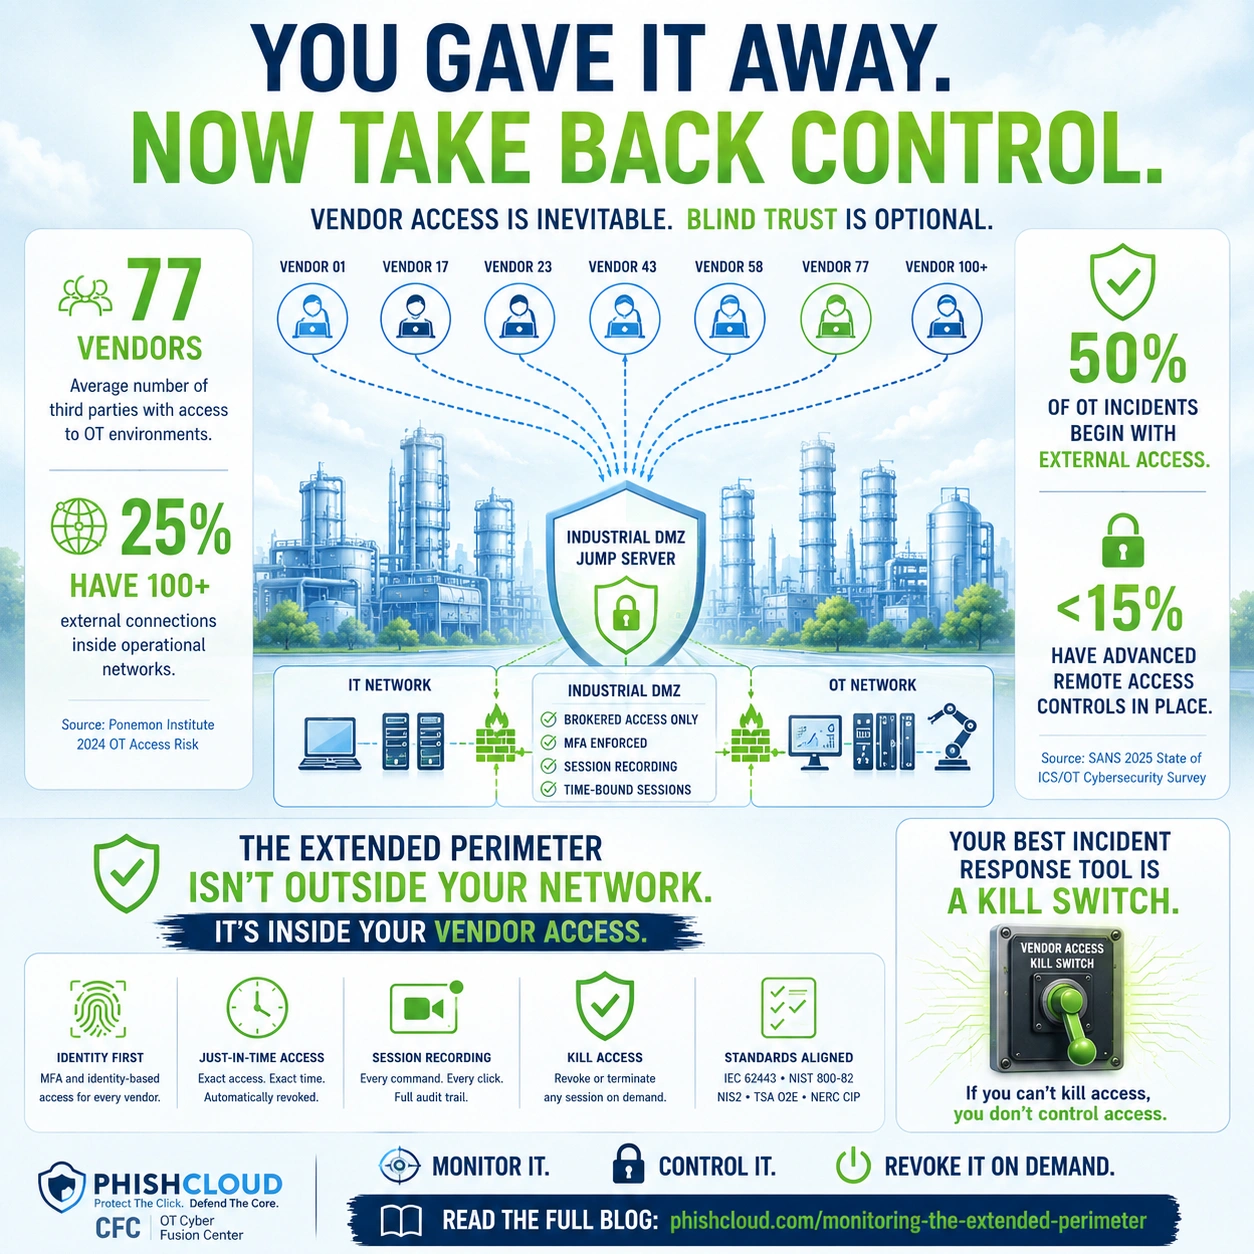
Monitoring the Extended Perimeter: The CFC and OT Vendor Access
Industrial organizations now grant an average of 77 vendors access to OT environments, and half of OT incidents begin through unauthorized external pathways.
Incident Response · Governance & Compliance
 Governance & Compliance
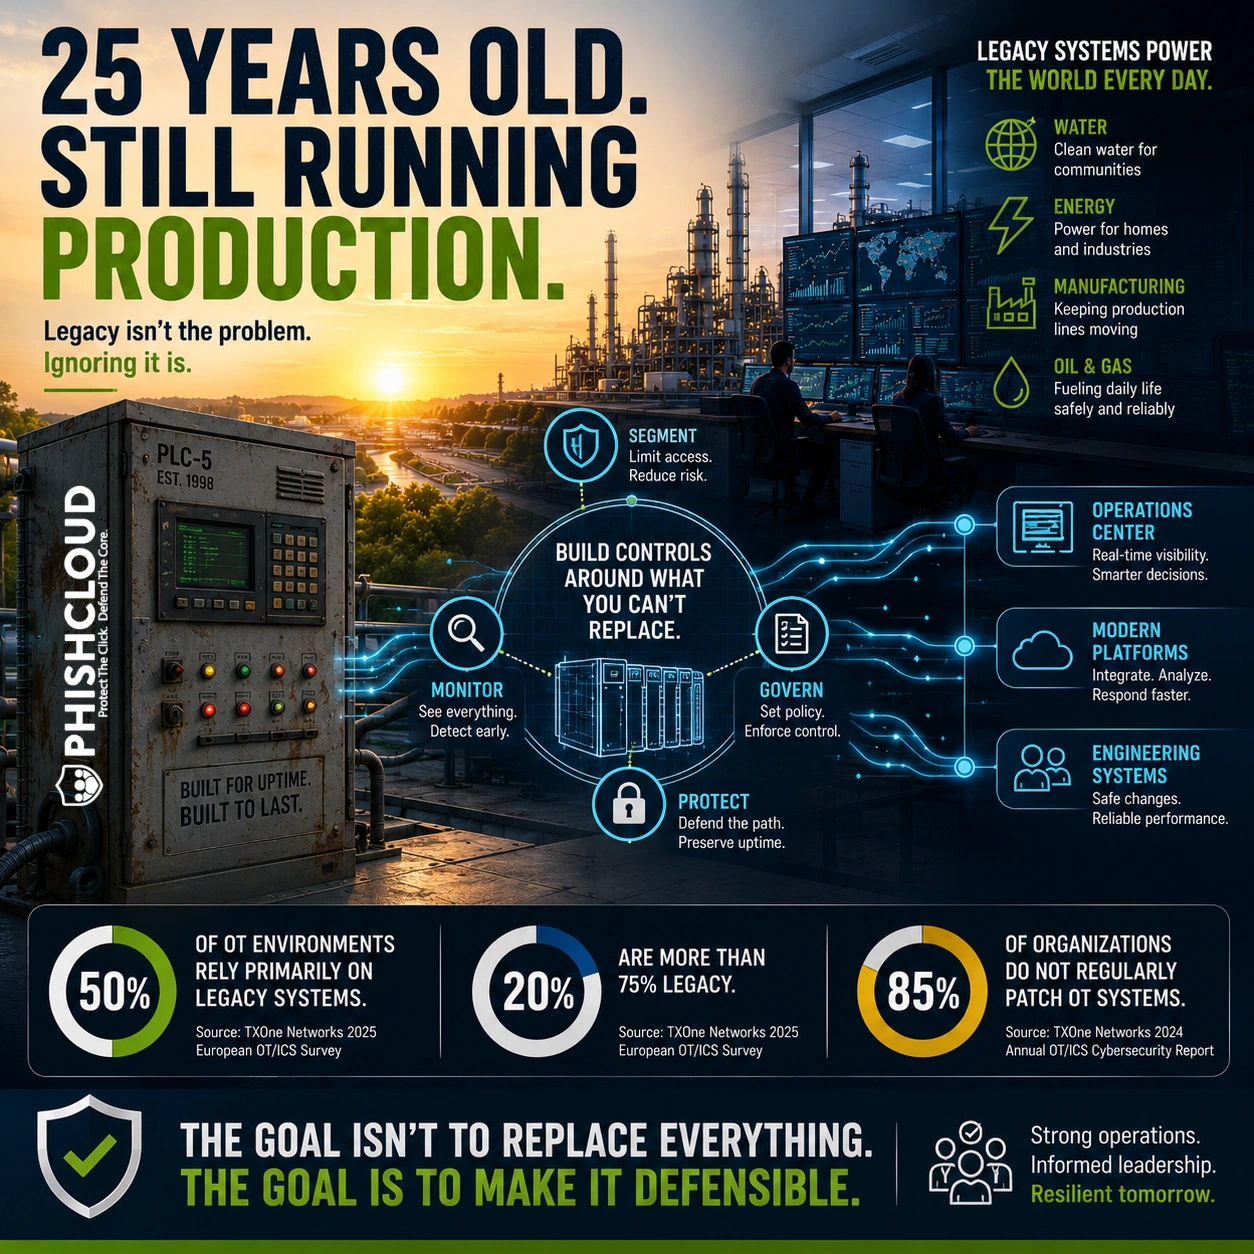
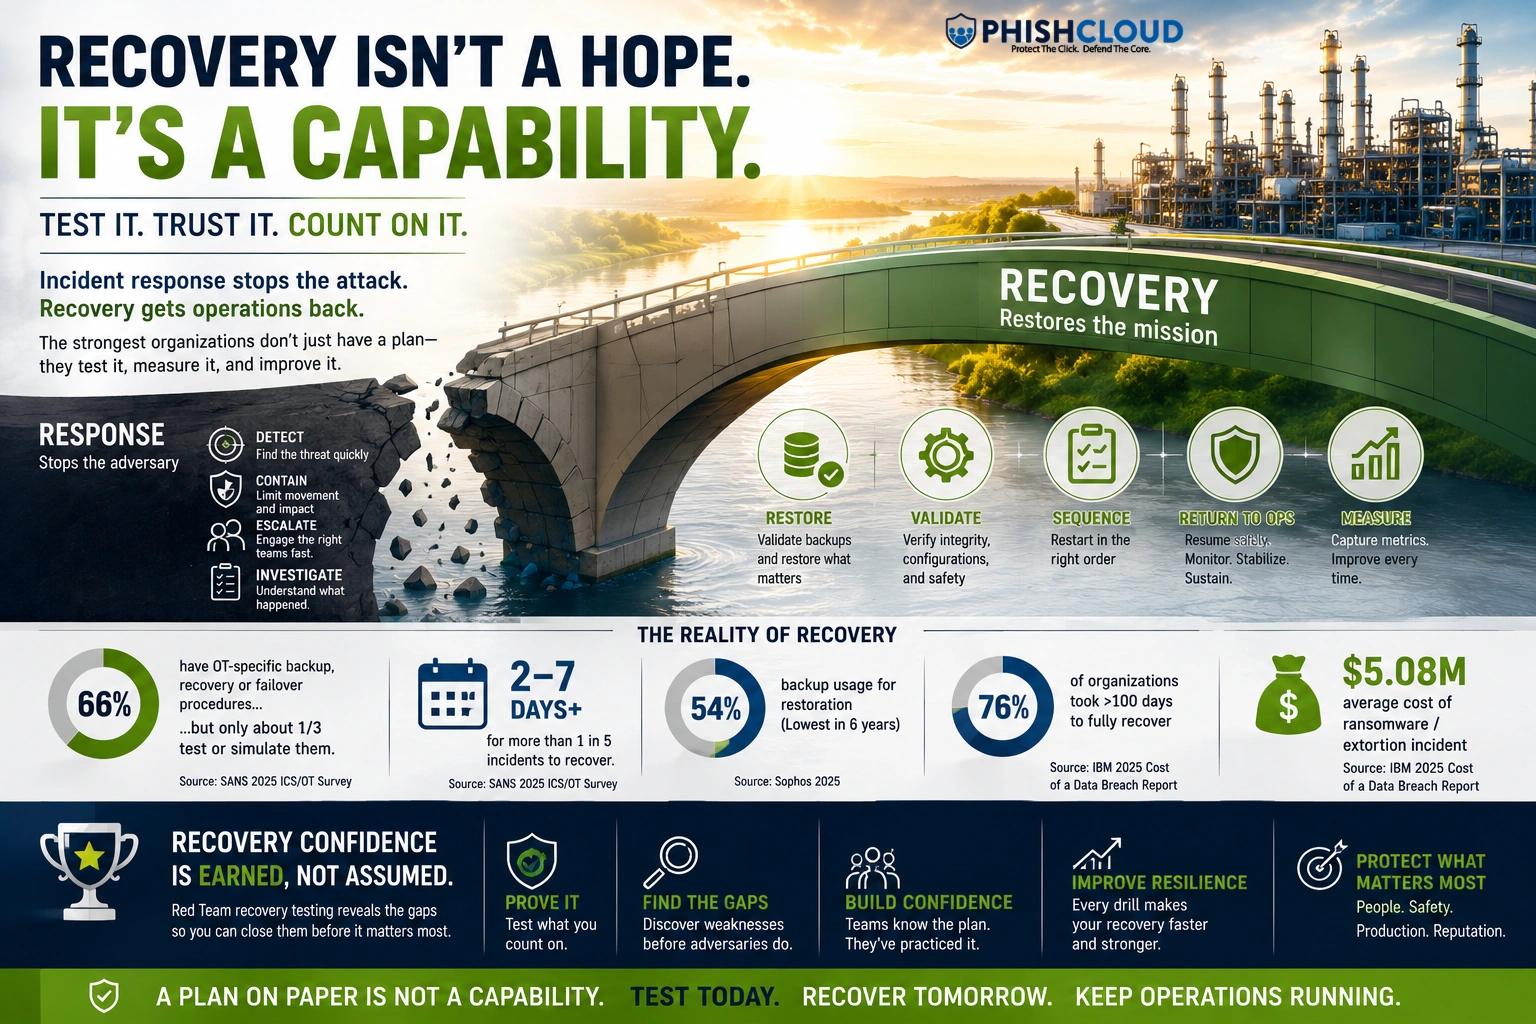
Why Legacy Is Every Red Team's Favorite OT Finding
CISA documented a Red Team living undetected for three months inside an OT environment with no EDR. That was not an anomaly.
 Detection & Monitoring
Owning the Vendor Risk
Vendor access is the OT pathway nobody can remove and too few can govern. After Cyber Av3ngers exploited default credentials and exposed U.S.
Incident Response · Governance & Compliance
 Detection & Monitoring
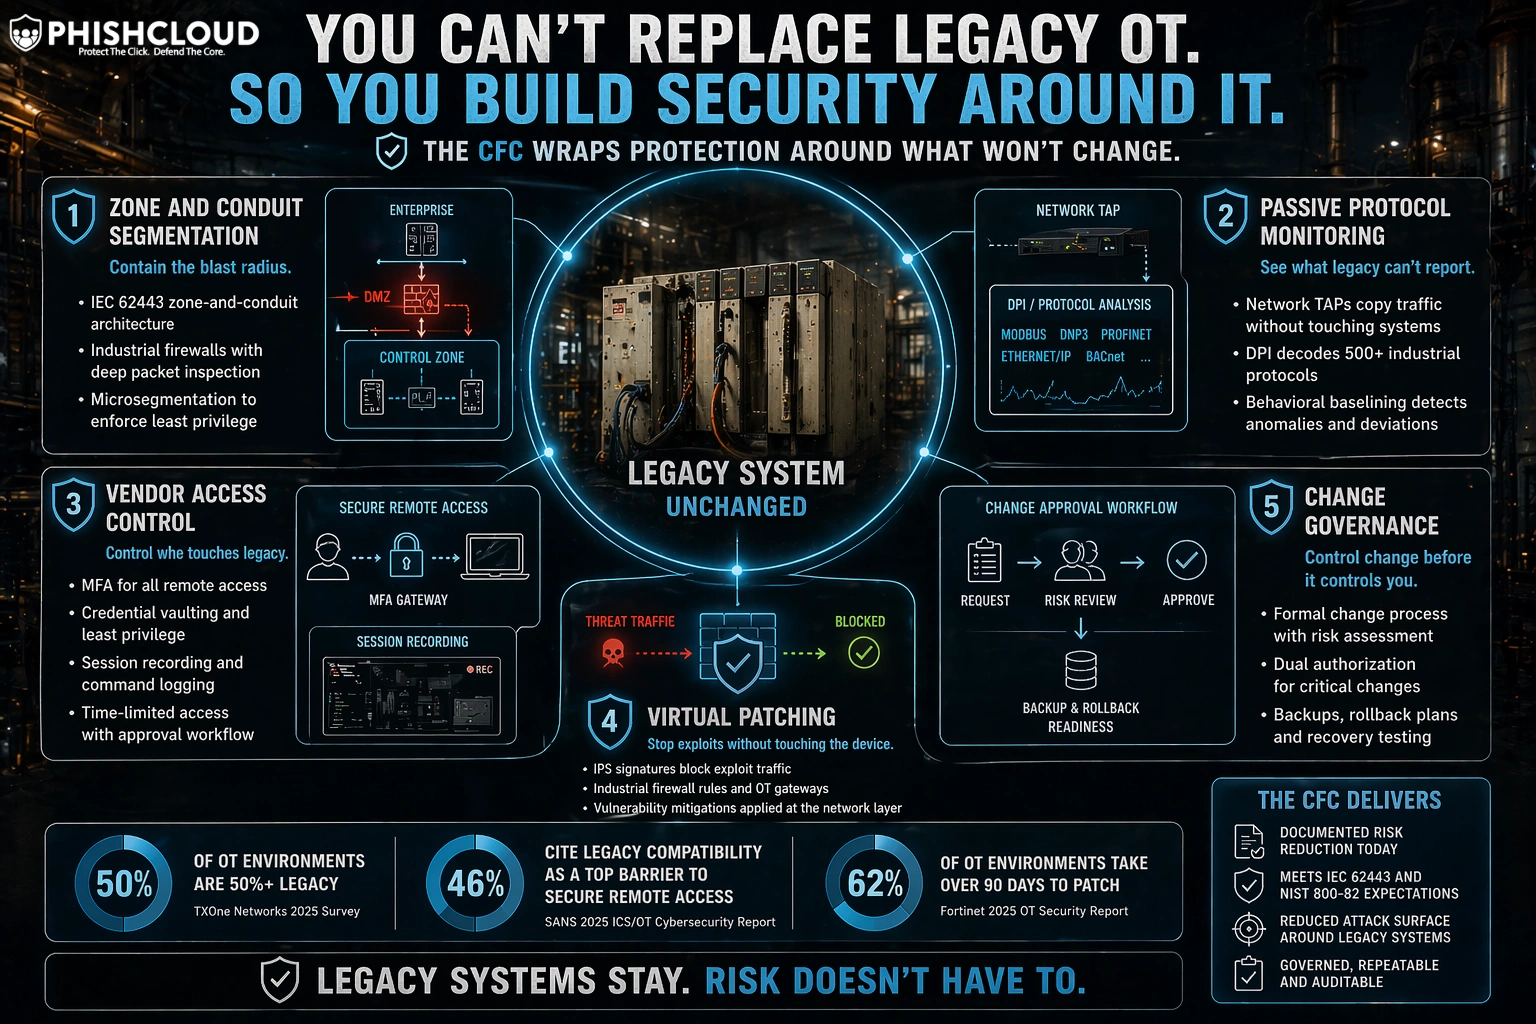
Building Around What Won't Change
Modbus is 47 years old and still shipping on new industrial equipment. Half of OT environments run on legacy systems that can't accept endpoint agents, won't tolerate active scanning, and go years without patches.
Governance & Compliance · Risk & Leadership
 Detection & Monitoring
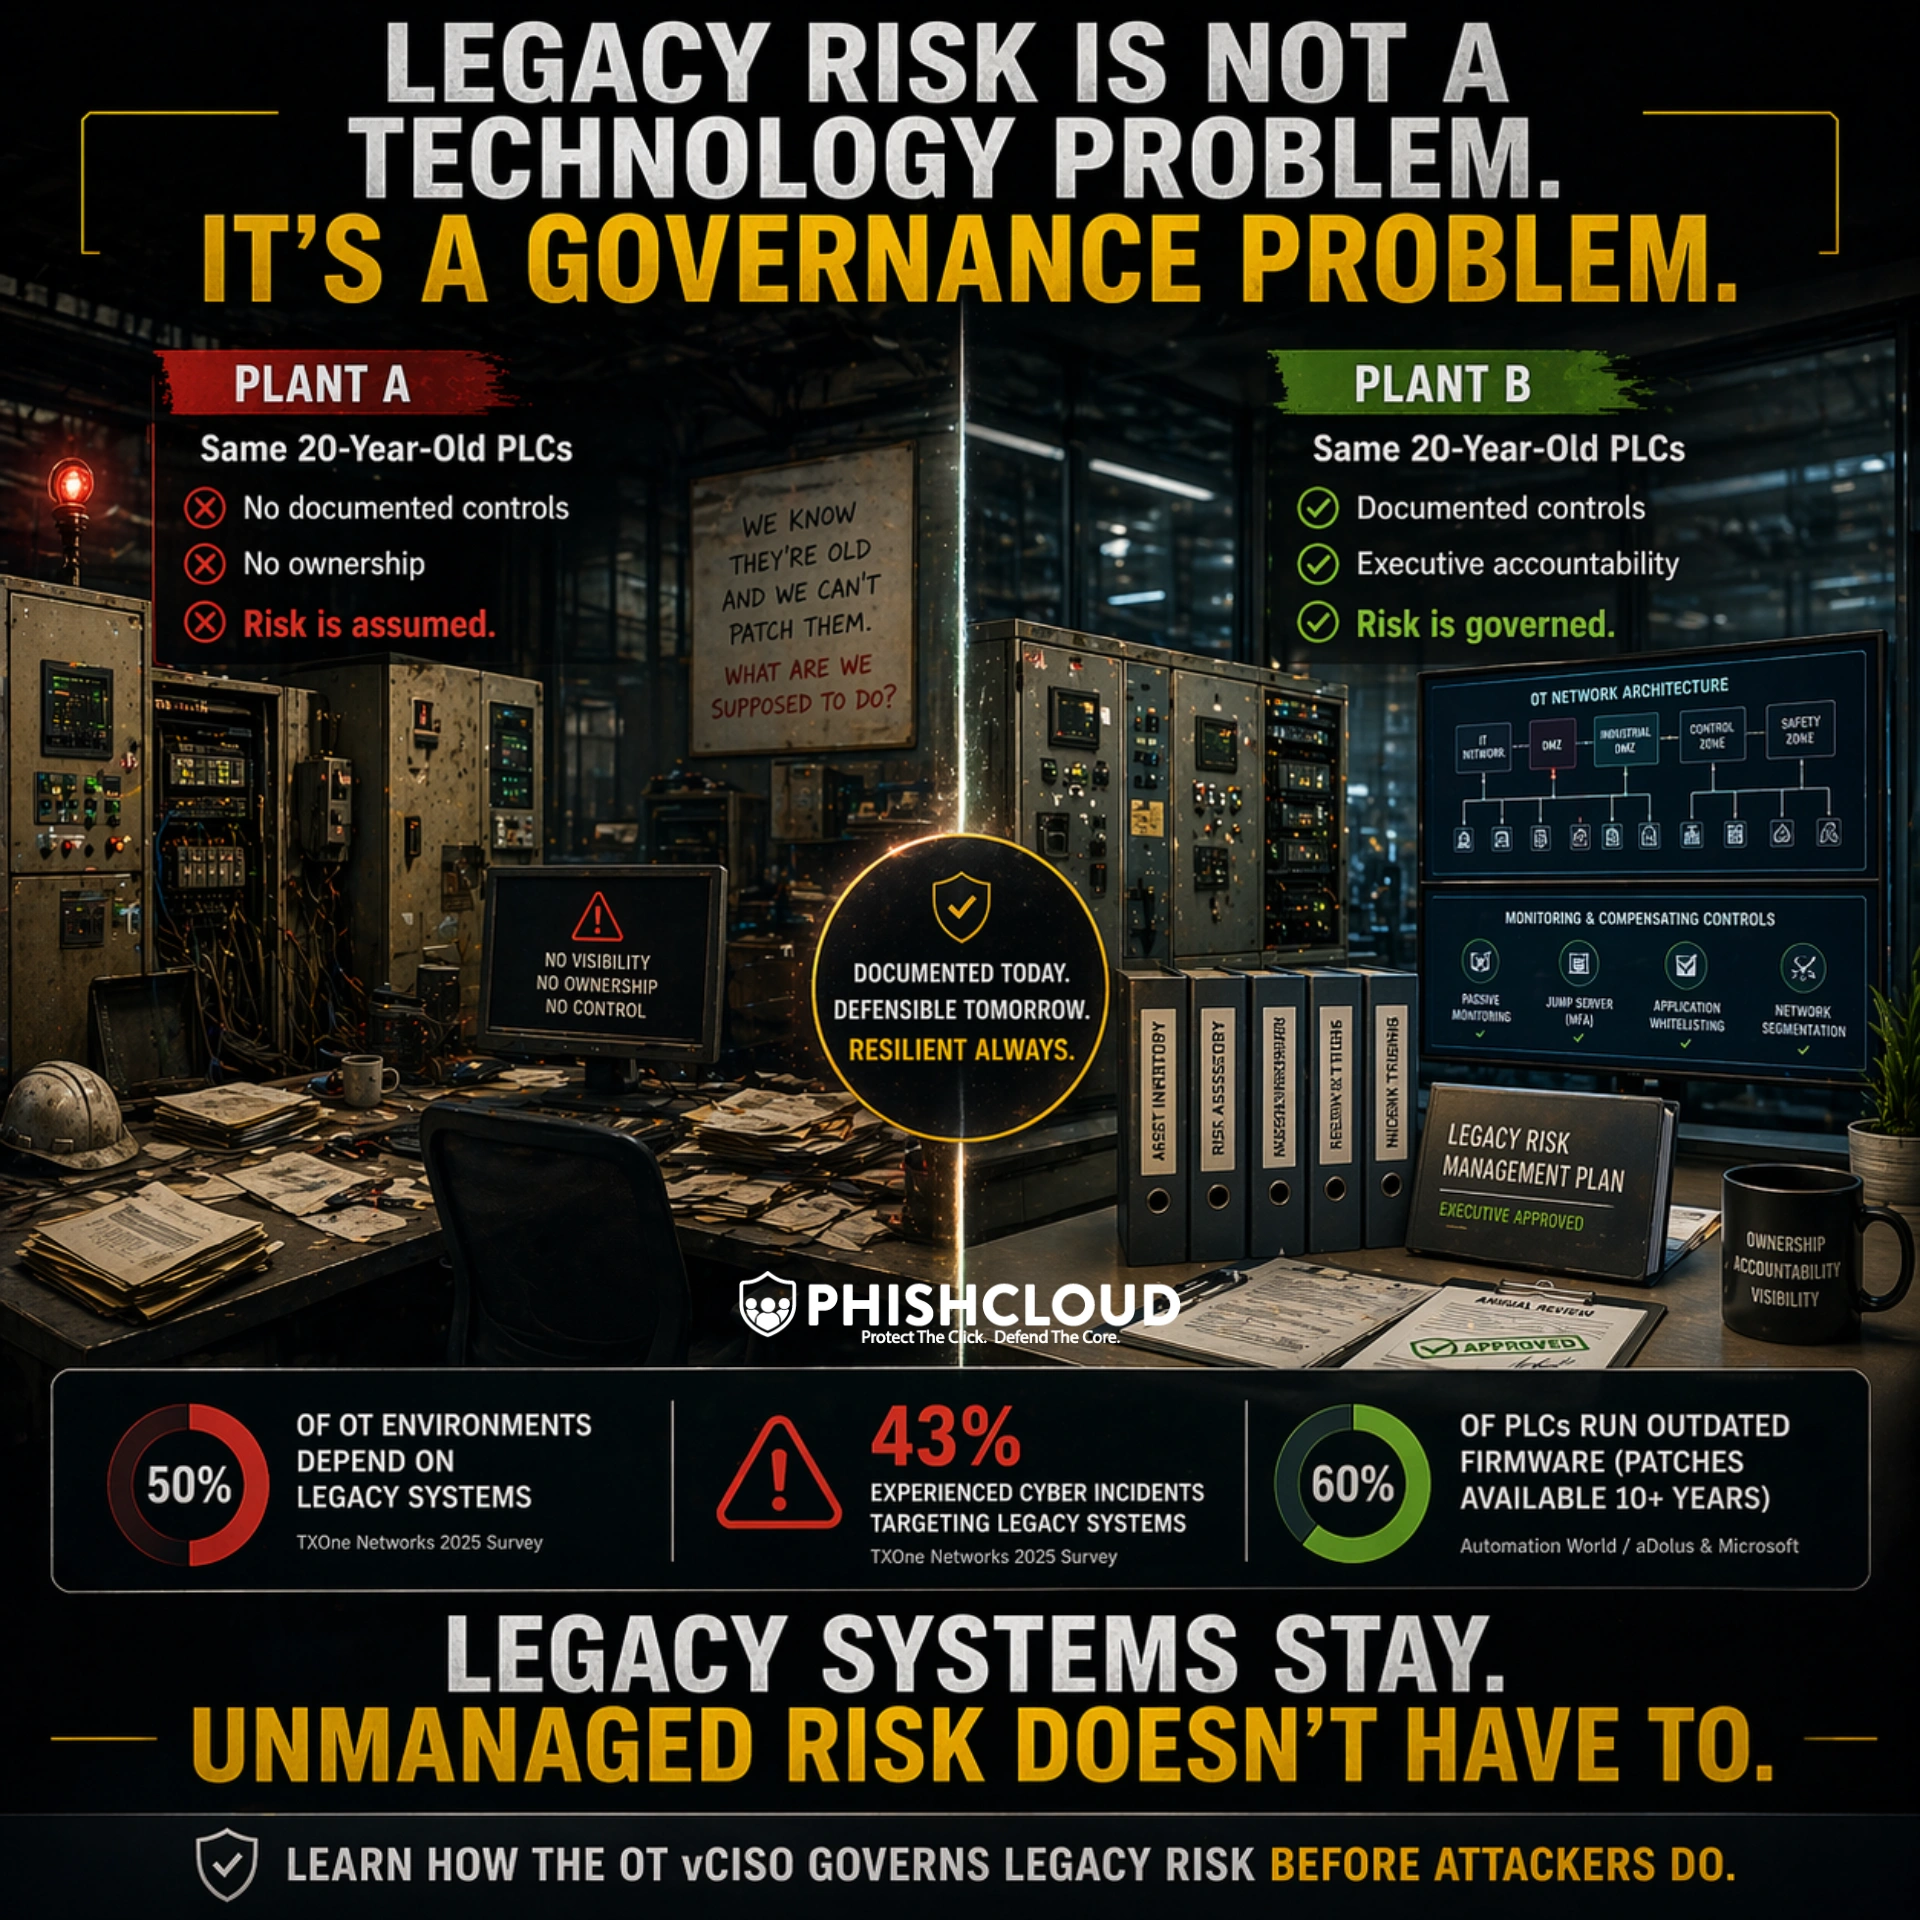
Governing Legacy OT Risk
43% of industrial organizations experienced a cyber incident targeting legacy OT last year. Half run on systems they can't patch.
Governance & Compliance · Risk & Leadership
 Detection & Monitoring
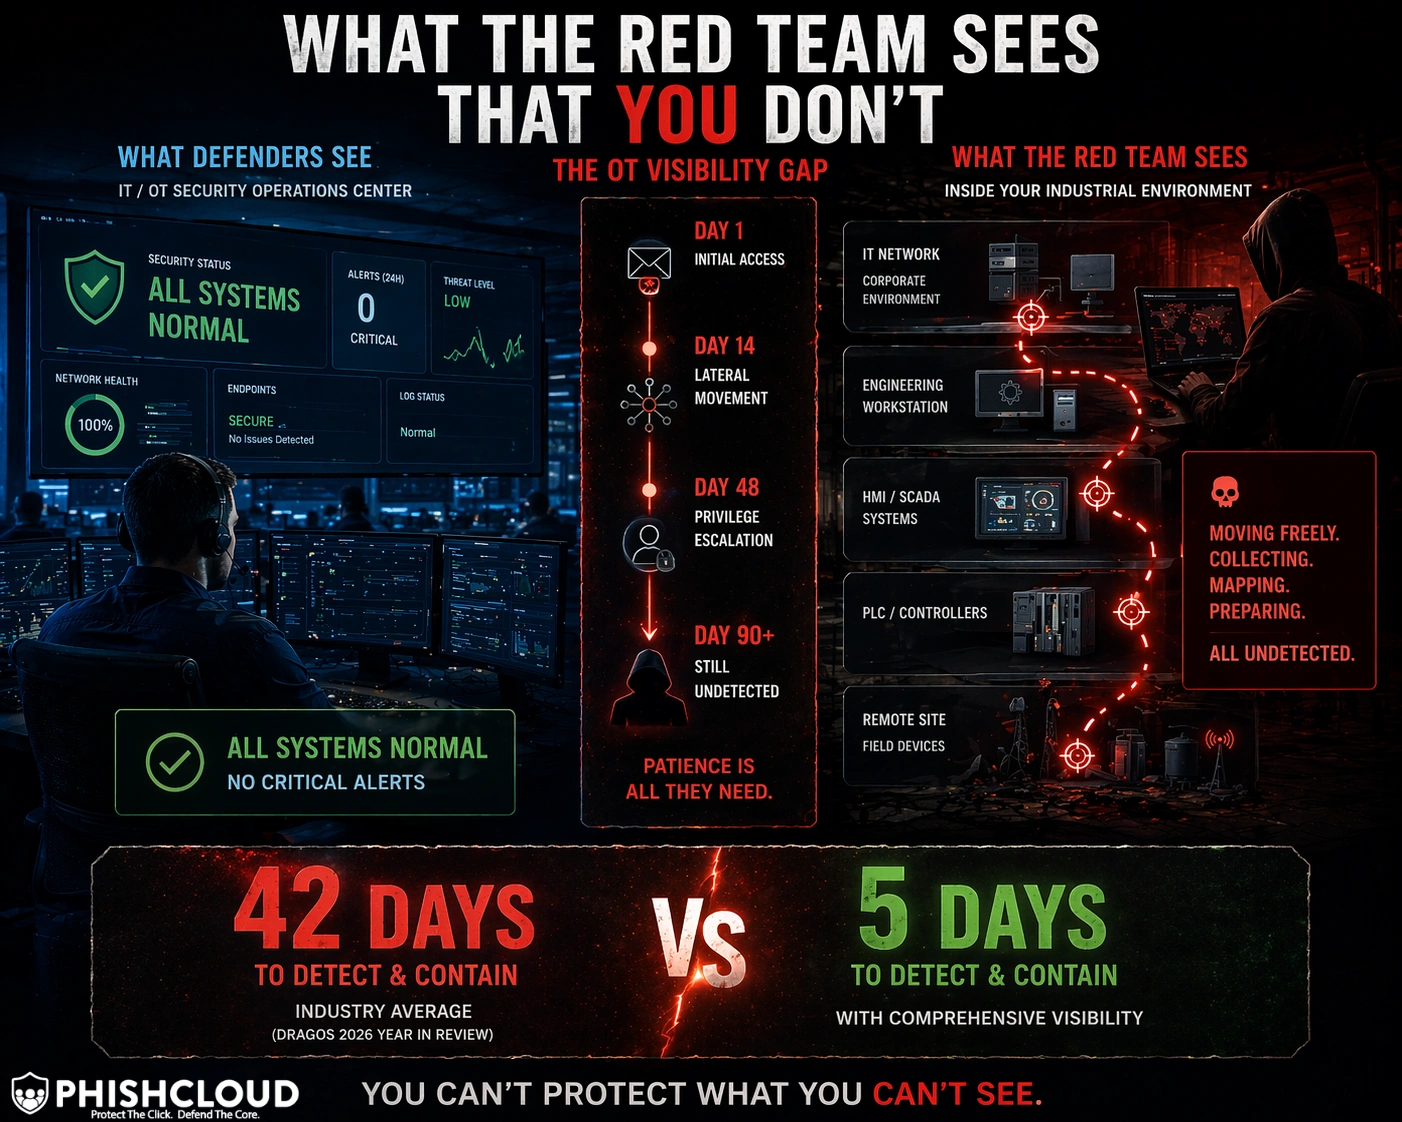
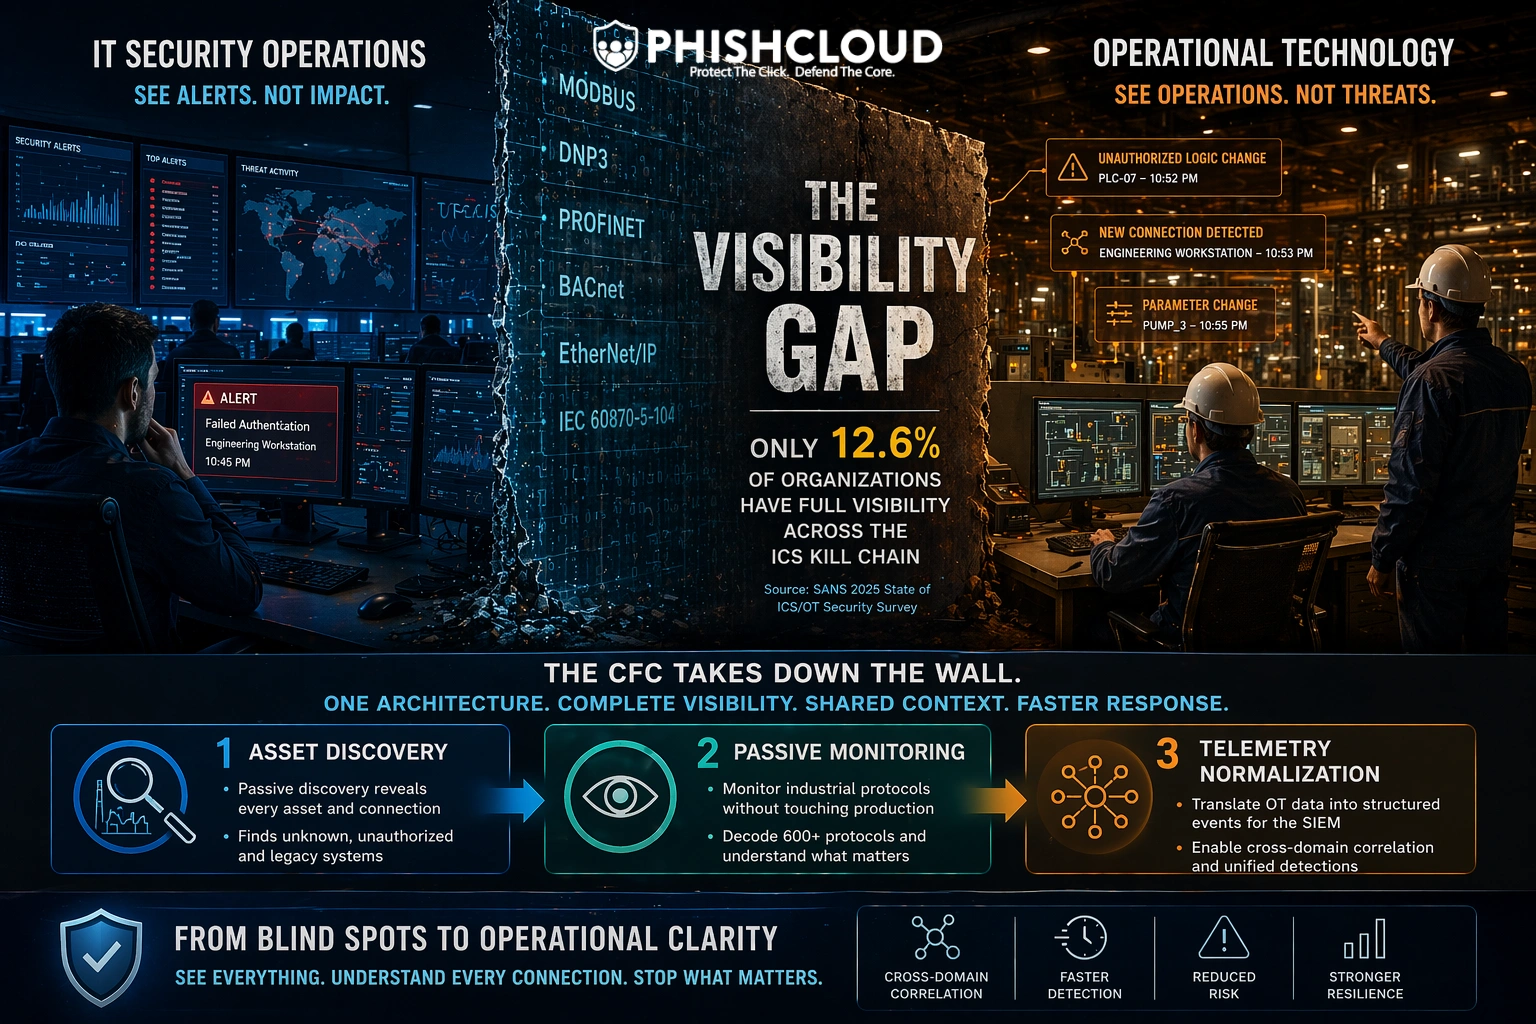
What the Red Team Sees That You Don't: The OT Visibility Gap
Organizations with weak OT visibility give adversaries weeks inside industrial environments before anyone sees movement.
 Detection & Monitoring
The CFC as OT Visibility Architecture
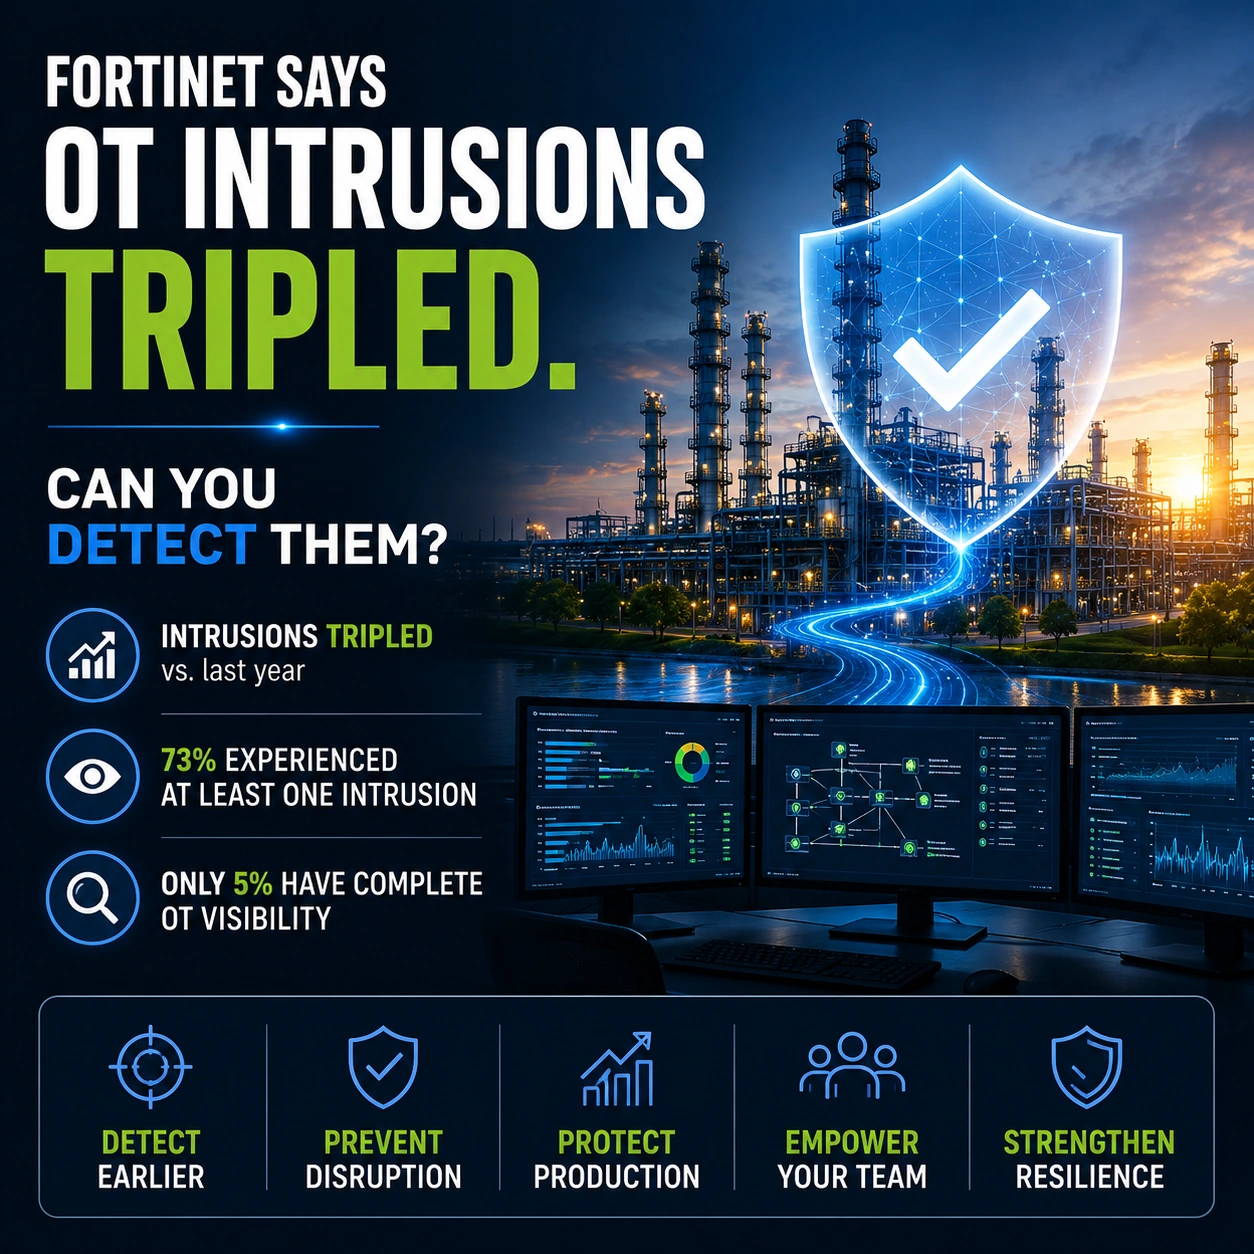
Only 12.6% of industrial organizations can see across the full ICS Kill Chain, leaving attackers room to move from IT into OT undetected for weeks.
Incident Response · Governance & Compliance
 Detection & Monitoring
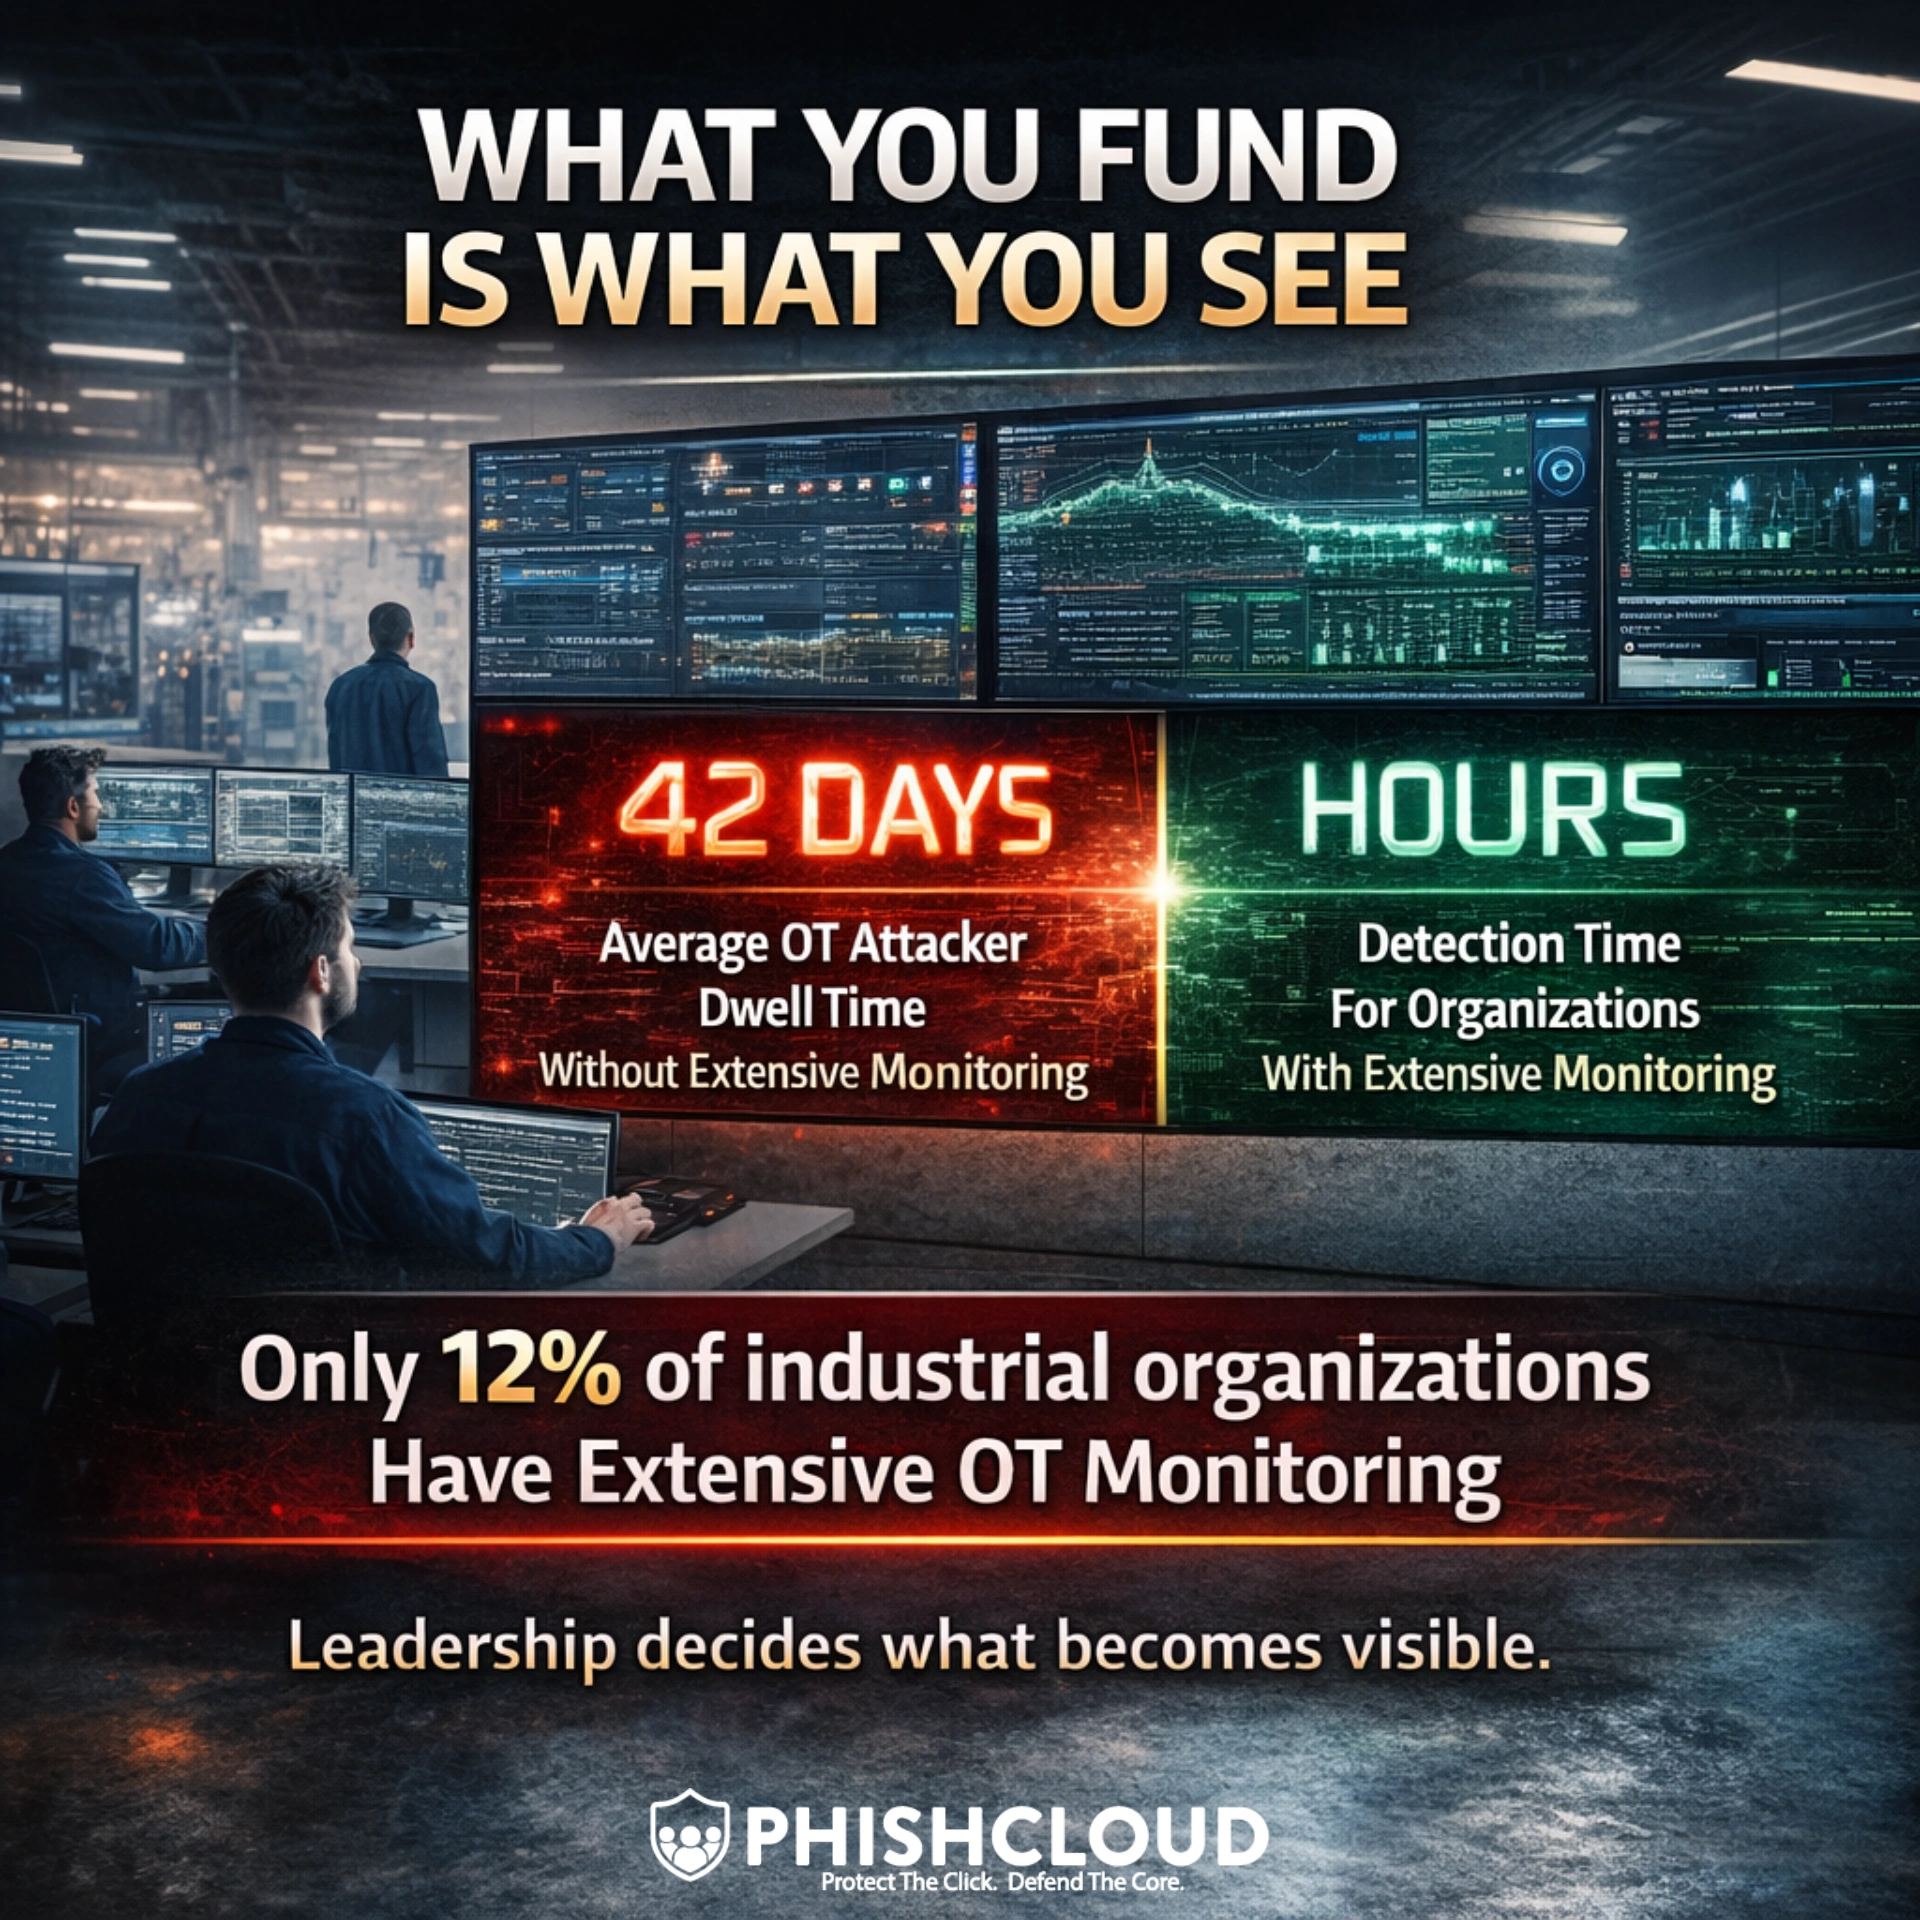
What You Fund Is What You See
Only 12% of industrial organizations have extensive OT monitoring, and the rest average 42 days of attacker dwell time.
Incident Response · Governance & Compliance · Risk & Leadership
 OT & ICS
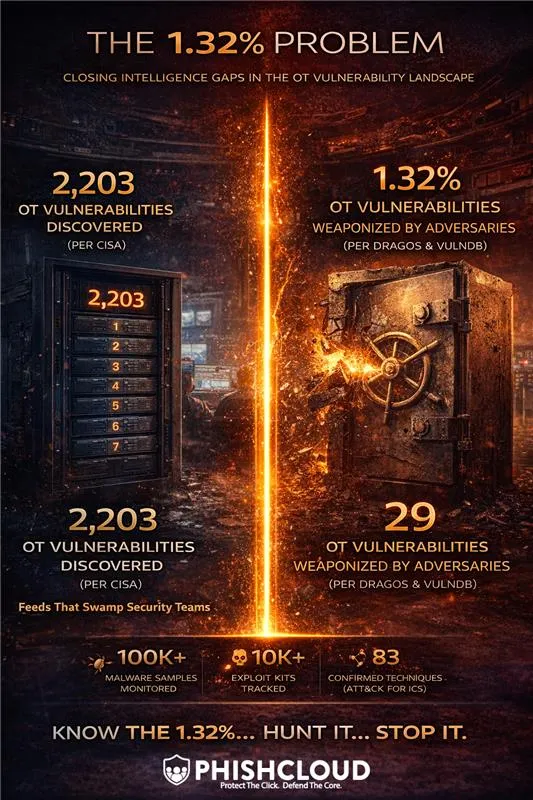
How Red Teams Validate Your OT Threat Intelligence
In late 2024, CISA's red team assessed a critical infrastructure organization with regular pen tests, active EDR, and a mature security posture by every documented measure.
Detection & Monitoring · Incident Response · Ransomware · Governance & Compliance · Threat Intelligence
 Detection & Monitoring
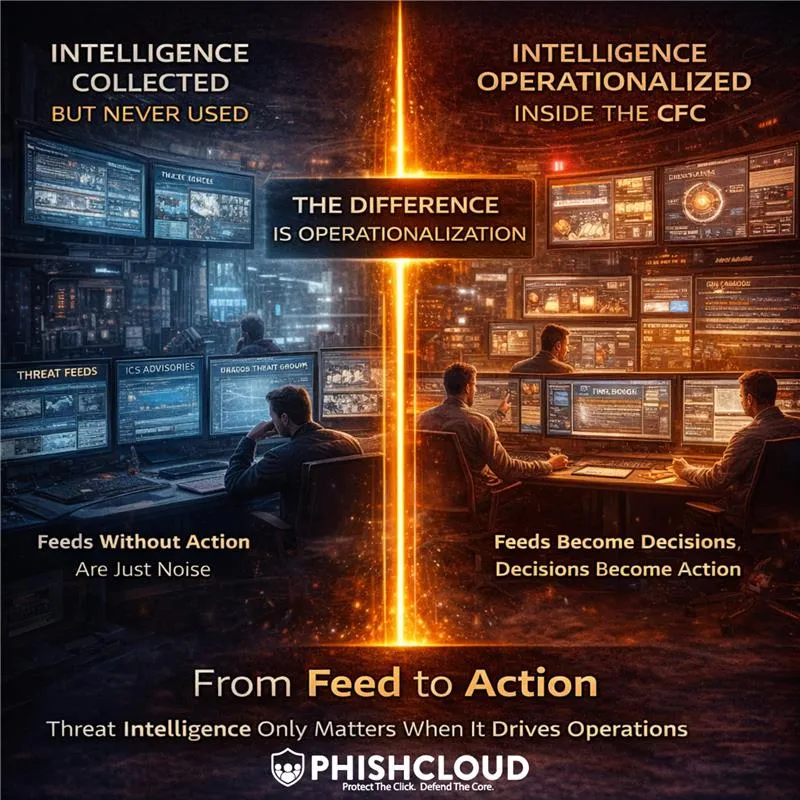
The CFC Blueprint
In 30% of Dragos incident response cases from 2025, investigations didn't begin with a detection alert. Those organizations subscribed to feeds and received advisories. The information existed.
Incident Response · Threat Intelligence
 Detection & Monitoring
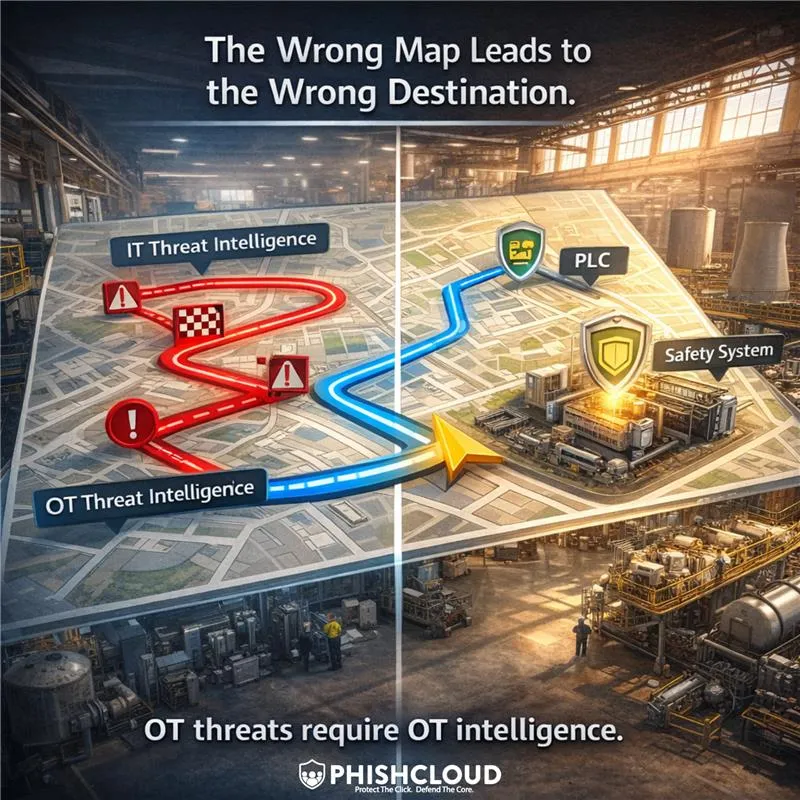
Intelligence That Actually Fits
OT threat intelligence is structured differently from generic IT feeds, because the problem is different.
Incident Response · Ransomware · Threat Intelligence · Risk & Leadership
 Detection & Monitoring
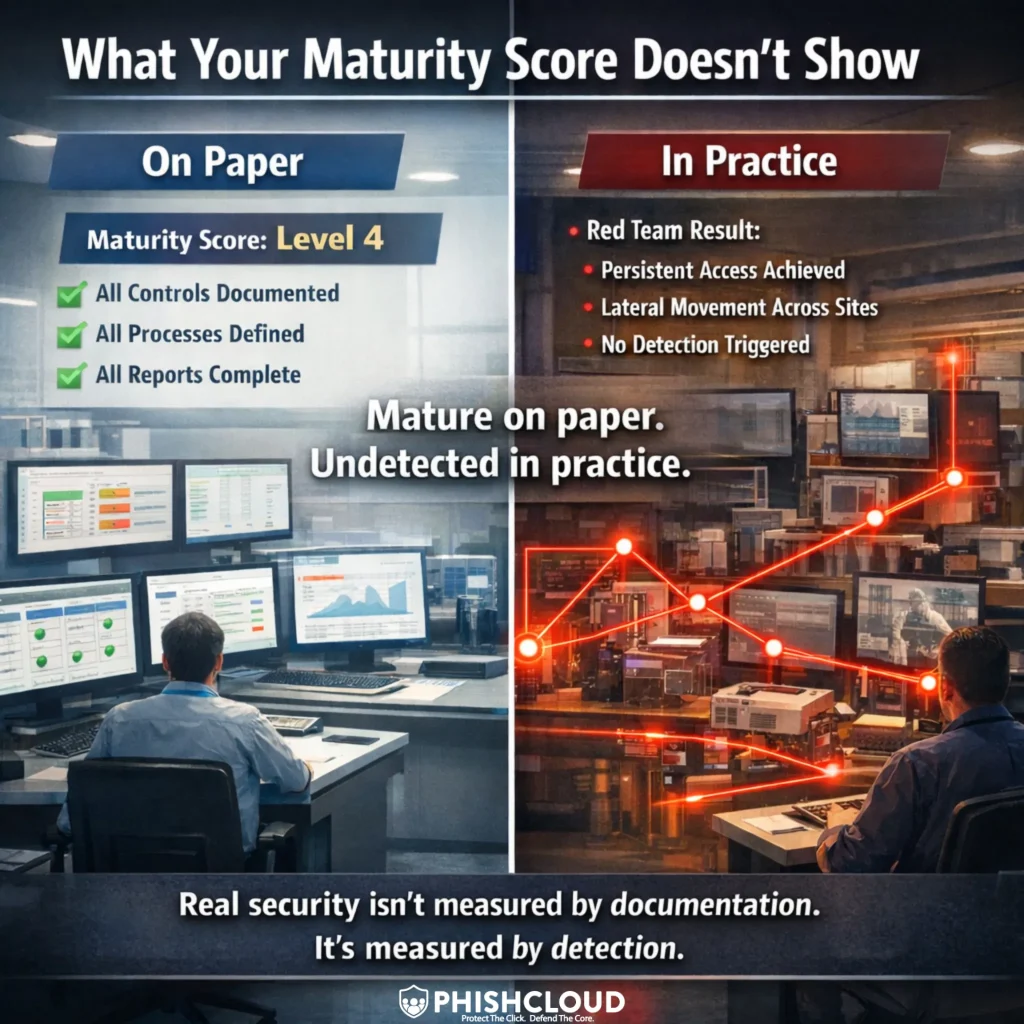
What Your Maturity Score Doesn't Show
CISA's red team assessed a large critical infrastructure organization in 2022. Leadership called their posture mature.
Incident Response · Ransomware · Governance & Compliance · Threat Intelligence
 OT & ICS
Change Your Roadmap
81% of organizations self-assess their OT security maturity at Level 3 or 4. SANS 2025 found only 12.6% with full ICS Kill Chain visibility. The gap isn't dishonesty.
Detection & Monitoring · Incident Response · Ransomware · Governance & Compliance
 Detection & Monitoring
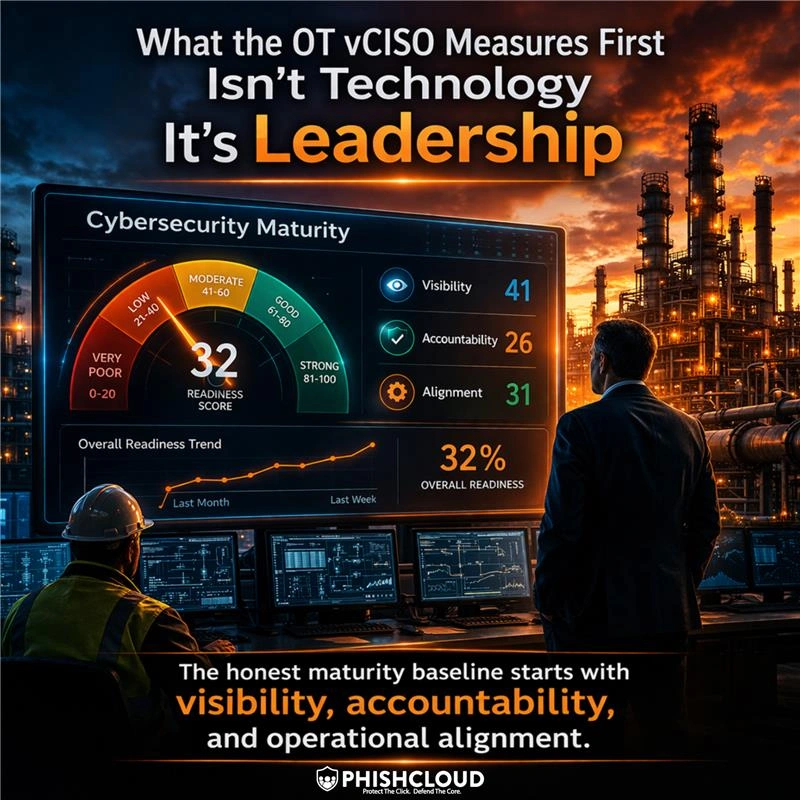
What the OT vCISO Measures First: The Honest Maturity Baseline
81% of industrial organizations rate their OT security maturity at Level 3 or 4. Only 5% can back it up with full asset visibility.
Incident Response · Governance & Compliance
 Detection & Monitoring
Who Owns OT Risk? What Red Team Tabletops Actually Find
A Red Team facilitator asks one question mid-simulation: who has authority to isolate the OT segment? The room goes quiet. That silence is a finding.
Incident Response · Ransomware · Governance & Compliance · Risk & Leadership
 Detection & Monitoring
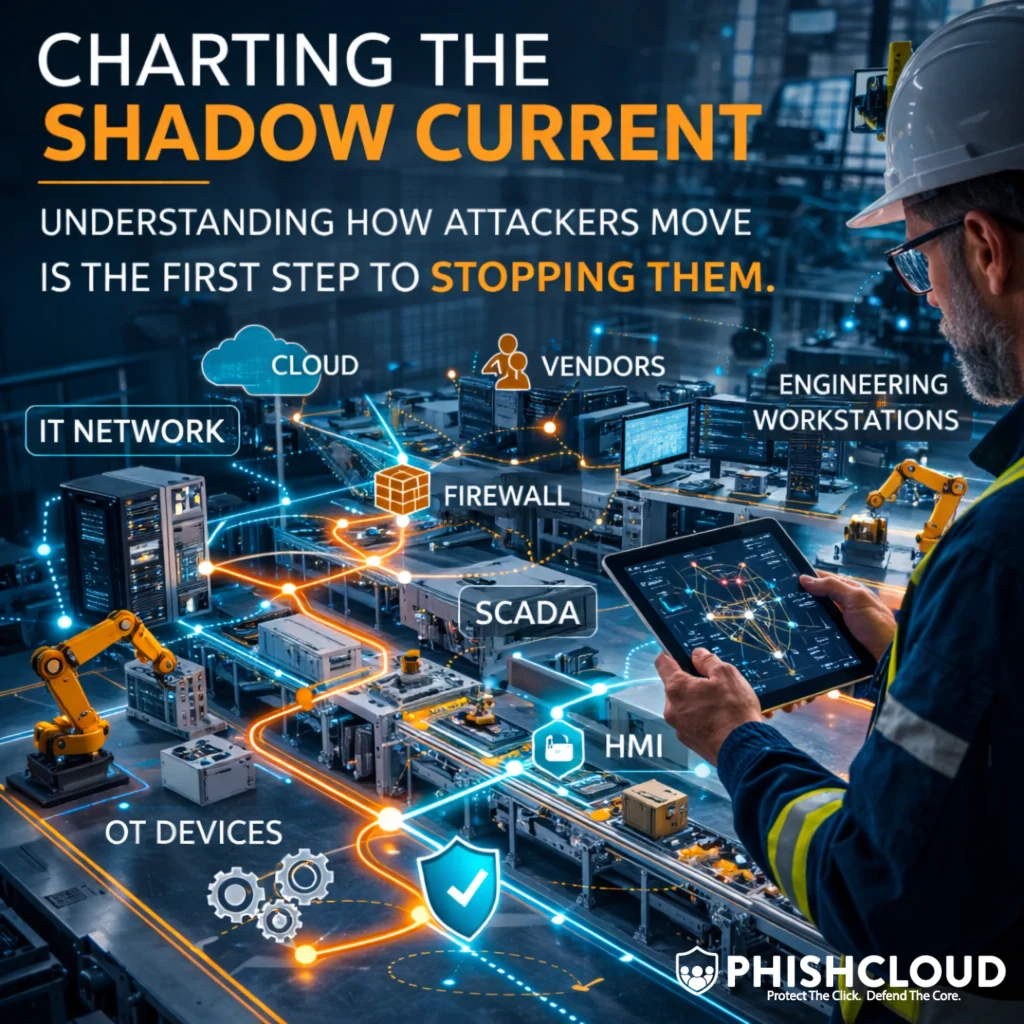
Charting Your Shadow Current: Speaking Leadership's Language
95% of CISOs brief their boards. Only 30% call it a strong relationship. The gap isn't data. It's translation.
Incident Response · Ransomware · Phishing & Email · Governance & Compliance · Risk & Leadership
 Detection & Monitoring
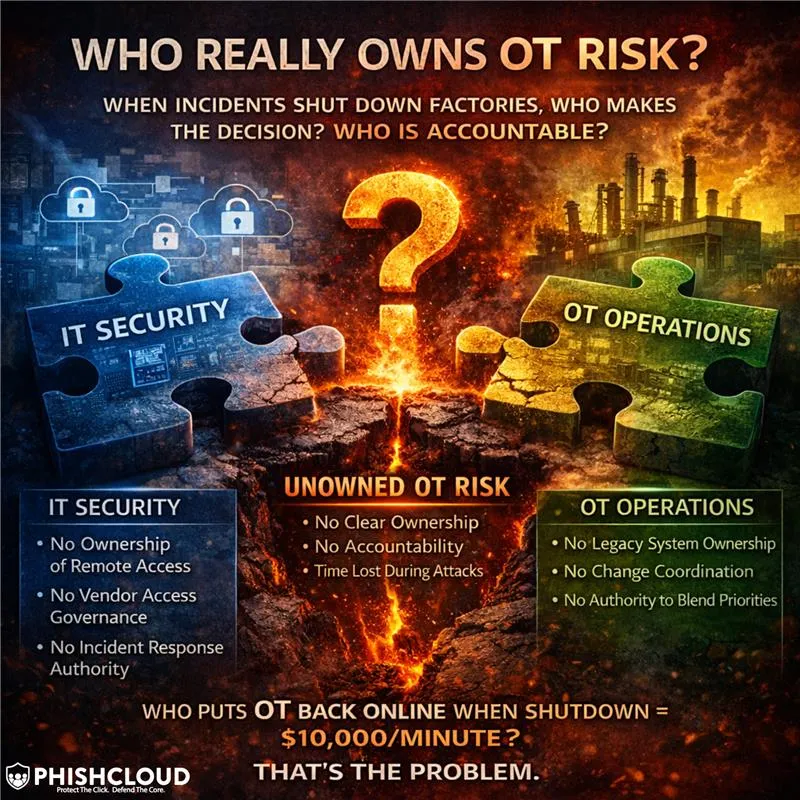
Mind The Gap: Who Owns What in OT Security?
Only 13% of OT attacks in 2024 directly touched OT systems. The other 87% caused physical impact through the IT boundary — the organizational seam nobody owns. Colonial Pipeline's OT was never compromised.
Incident Response · Governance & Compliance
 Incident Response
Fixing Vulnerabilities Doesn’t Fix the System
Attackers weaponized vulnerabilities before patches existed — Mandiant clocked average time-to-exploit at negative one day in 2025. But patching still wouldn't have closed the channel.
Ransomware
 Incident Response
The Accountability Map: Who Really Owns OT Risk?
Colonial Pipeline's OT was never breached. The pipeline shut down anyway — because no one could answer a single question: is OT safe to keep running? That's not a technical failure. It's an accountability failure.
Governance & Compliance · Threat Intelligence
 Detection & Monitoring
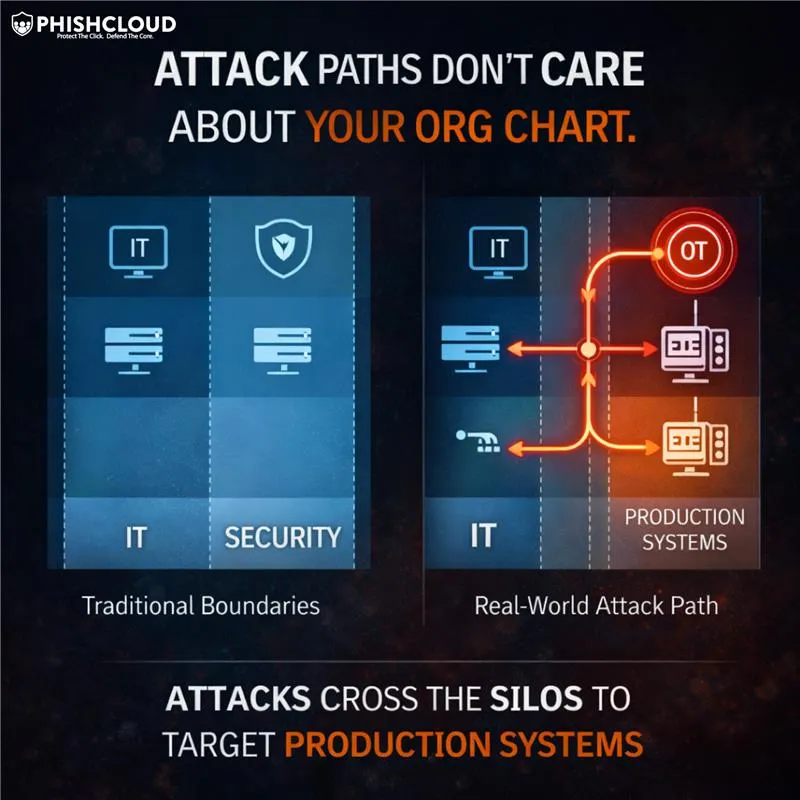
Attack Paths Don't Care About Your Org Chart
Your IT team stops at the network boundary. Your OT team stops at the plant floor. Attackers stop for neither.
Incident Response · Ransomware · Governance & Compliance · Threat Intelligence
 Incident Response
Exposing the Leadership Gap
The first question on the OT red team scoping call — who owns this, who decides, who acts — is already the first finding. CISA's 2024 assessment found that leadership deprioritized a flagged vulnerability.
Governance & Compliance · Risk & Leadership
 OT & ICS
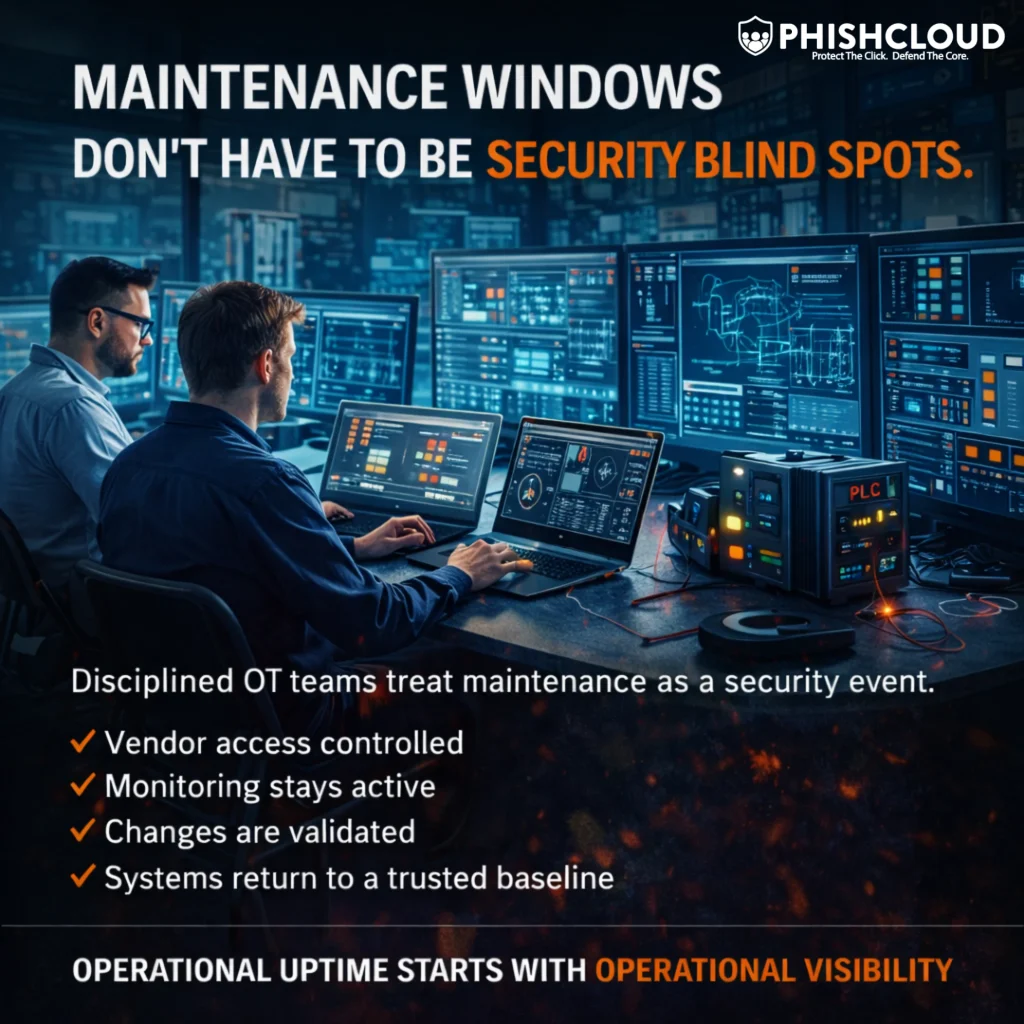
Your Maintenance Window Is an Open Invitation to Attackers
A contractor's USB drive brought a petrochemical facility down for three weeks—no zero-day required.
Detection & Monitoring · Incident Response · Governance & Compliance
 Detection & Monitoring
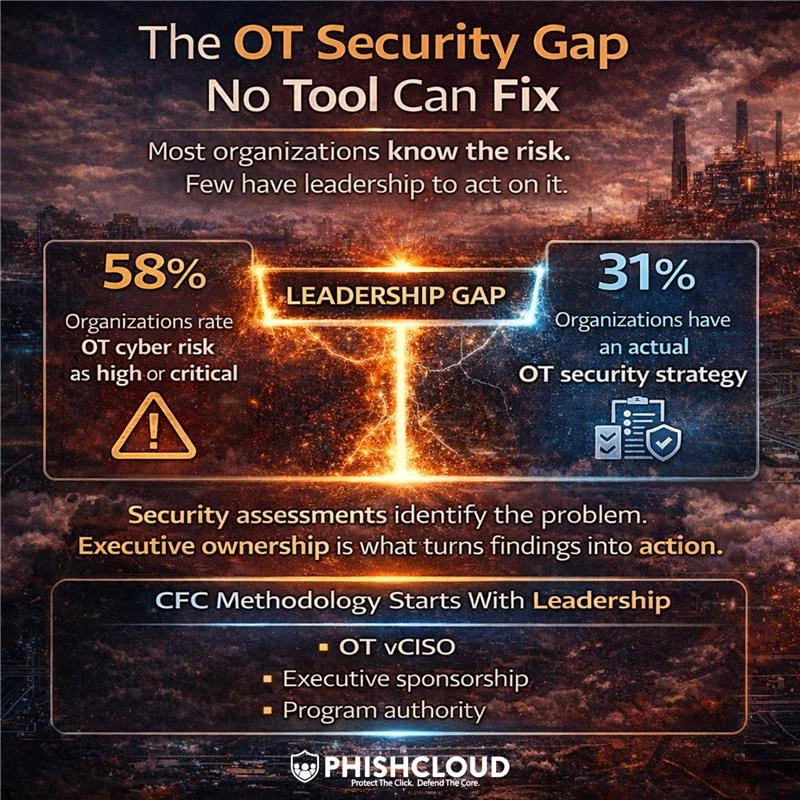
The Missing Executive That's Killing Your OT Security Strategy
Seventy-one percent of organizations have OT security assessments gathering dust in shared drives.
Governance & Compliance · Risk & Leadership
 Detection & Monitoring
Pentests Don't Map Shadow Currents. Attackers Do.
96% of organizations change their IT environment quarterly. Most pen test annually. By the time the report lands, 40% of results are already invalid.
Incident Response · Governance & Compliance
 OT & ICS
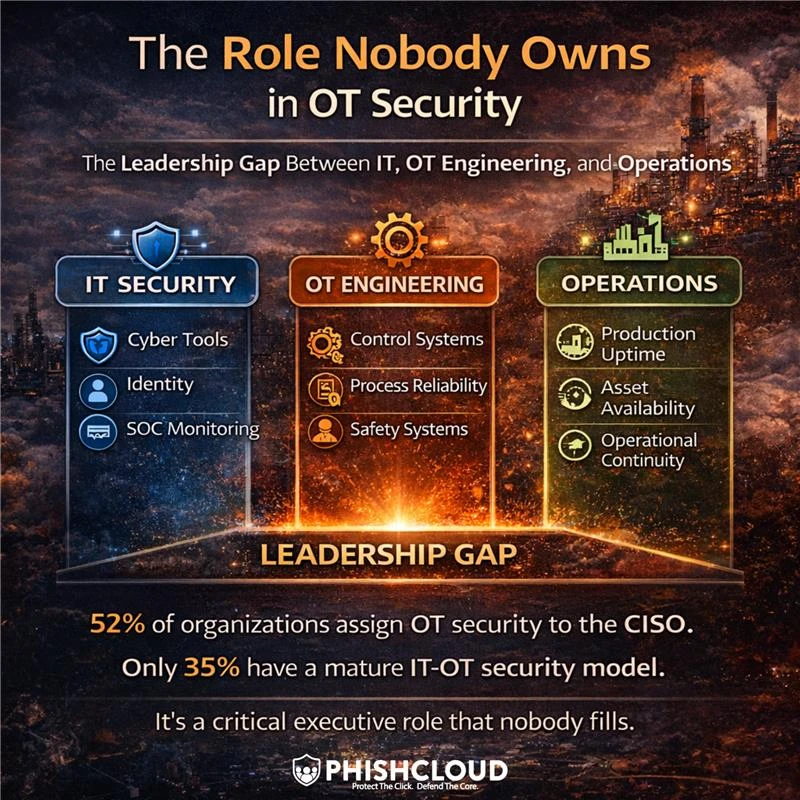
The Role Nobody Owns
52% of organizations now assign OT security to the CISO. Only 35% have the capability to back it up. The title changed. The leadership didn't follow.
Detection & Monitoring · Incident Response · Ransomware · Governance & Compliance · Risk & Leadership
 OT & ICS
Passing the Audit, Failing the Attack Path Test
Ukraine's electric utility passed every compliance check on December 23, 2015. 225,000 customers lost power anyway.
Detection & Monitoring · Incident Response · Governance & Compliance
 OT & ICS
Living Off the Land: How Iran Turned Stryker's Security Tools Into a Weapon
Iran-linked Handala didn't hack Stryker. They logged in. Using one compromised admin account and Microsoft Intune's "remote wipe" button, they simultaneously erased 200,000 devices across 79 countries. No malware.
Detection & Monitoring · Incident Response · Ransomware · Threat Intelligence
 Detection & Monitoring
Third-Party Vendor Access: The Shadow Current to Your OT
Seventy-three percent of industrial organizations hand their critical systems to an average of 77 outside vendors—then stop watching.
Incident Response · Ransomware
 OT & ICS
The Legacy Shadow Current
Windows XP turns 25, yet still runs critical infrastructure in power plants and manufacturing facilities.
Detection & Monitoring
 Detection & Monitoring
Why Credential Theft Carries the Shadow Current
292 days. That's how long stolen credentials flow undetected through your infrastructure.
Incident Response · Ransomware · Phishing & Email
 OT & ICS
From Email to Outage: How the Shadow Current Starts in IT
22.5% of internet crimes start with phishing. When Anton Paar clicked one link, multi-site manufacturing collapsed within days. Colonial Pipeline fell in eight days.
Incident Response · Ransomware · Phishing & Email
 OT & ICS
The Air Gap That Wasn't
Dragos declared "we have never found an organization that is truly air-gapped," exposing industrial security's deadliest myth.
Detection & Monitoring · Incident Response · Ransomware · Governance & Compliance
 OT & ICS
The IT→OT Attack Path Everyone Has and Almost No One Tests
A single VPN password. No multi-factor authentication. That's all it took to trigger the Colonial Pipeline shutdown in May 2021, cutting fuel supplies across
Detection & Monitoring · Incident Response · Ransomware · Governance & Compliance
 Detection & Monitoring
The Shadow Current Map: Why Your Network Diagram Is Lying to You
Attackers achieve lateral movement in 48 minutes. Your security team detects it in 10 days.
Incident Response · Ransomware
 Incident Response
Shadow Currents: The Invisible Paths Carrying Attackers Through Your Network
Defenders patch in 16 days, attackers exploit in 5. With 80% of exploits weaponized before CVEs existed and Change Healthcare's $22M loss to chained paths, vulnerability management can't win this speed race.
Ransomware
 OT & ICS
Skeleton Crews, Full-Scale Attacks: The Holiday OT Security Gap
86% of ransomware attacks strike on weekends or holidays when 44% of organizations slash security staff by 70%. December 24th, 2024: Blue Yonder's Thanksgiving breach paralyzed Starbucks and UK supermarkets.
Detection & Monitoring · Incident Response · Ransomware
 OT & ICS
The Ghost of Christmas Future: How Red Team Assessments Reveal Tomorrow's OT Threats Today
Volt Typhoon lurked inside U.S. critical infrastructure for 5 years. FBI Director Wray called them "the defining threat of our generation.
Detection & Monitoring · Incident Response · Ransomware · Threat Intelligence
 Detection & Monitoring
Pen Tests Find Holes. Purple Teams Close Them.
Your red team documented critical vulnerabilities three weeks ago. Today, attackers exploited the exact same weaknesses.
Incident Response · Governance & Compliance
 Detection & Monitoring
Hours, Not Months: React2Shell Just Killed Quarterly Security
Within hours of December 3, 2025, China-nexus threat groups weaponized CVE-2025-55182—a CVSS 10.0 vulnerability affecting 39% of cloud environments and 2.15 million internet-facing services.
Threat Intelligence
 OT & ICS
Red Teaming for Reality: Human Blind Spots in OT Security
Ransomware surged 87% against industrial systems, hitting manufacturing hardest at 70%. But the real threat? IT professionals securing OT like corporate networks. Only 29% of facilities have OT expertise.
Detection & Monitoring · Incident Response · Ransomware · Phishing & Email · Governance & Compliance
 Detection & Monitoring
Inside the Attack Chain ⛓️
Over 46,000 industrial control systems exposed to the internet in 2024. Most had passed penetration tests. Attackers breach networks in 5 hours while defenders take 258 days to detect.
Incident Response · Ransomware · Threat Intelligence
 Detection & Monitoring
When Cybercrime Meets Organized Crime: The Rise of Cyber-Enabled Cargo Theft
See how cybercrime meets organized crime & the significant impact on industries, & how to protect your organization from these threats. Learn more here.
Threat Intelligence
 Detection & Monitoring
The Future of OT Security
Understand why cyber fusion centers are no longer optional, & how they are critical for securing operational technology in modern industries. Learn more here.
Ransomware
 OT & ICS
Beyond Compliance
OT Red Team assessments provide real resilience, going beyond compliance for true security protection. Learn more here.
Incident Response · Ransomware · Governance & Compliance
 OT & ICS
OT Red Team Assessment
When a single misconfigured PLC or weak VPN can halt production or endanger lives, OT environments can't rely on IT playbooks.
Detection & Monitoring · Incident Response · Phishing & Email · Threat Intelligence
 Detection & Monitoring
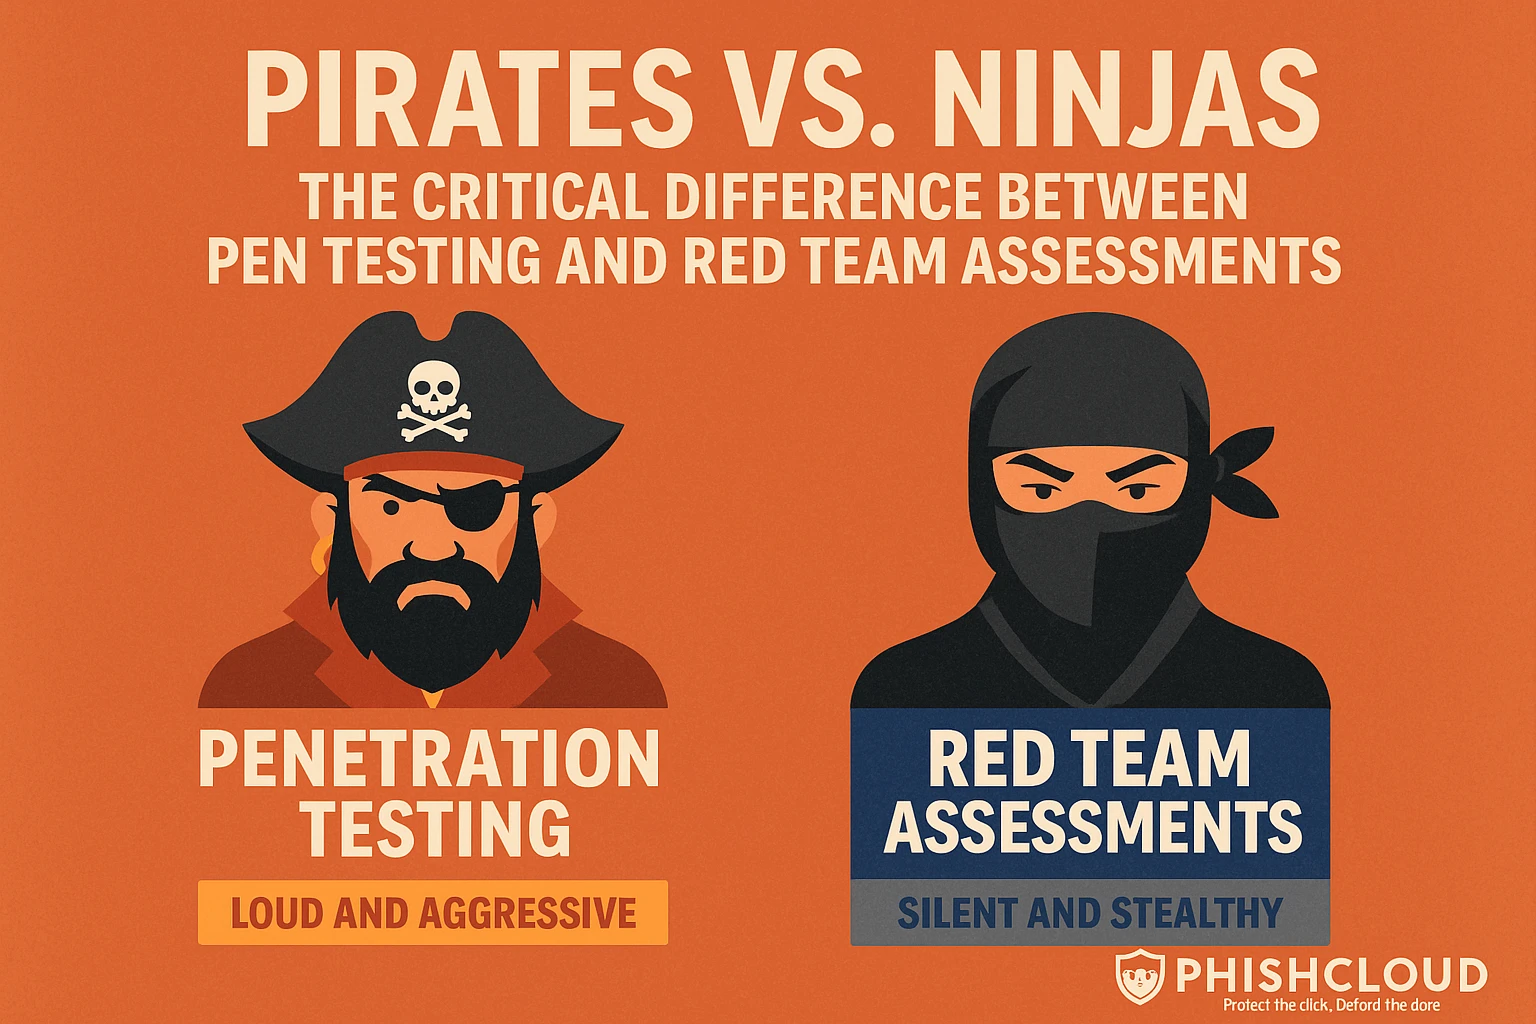
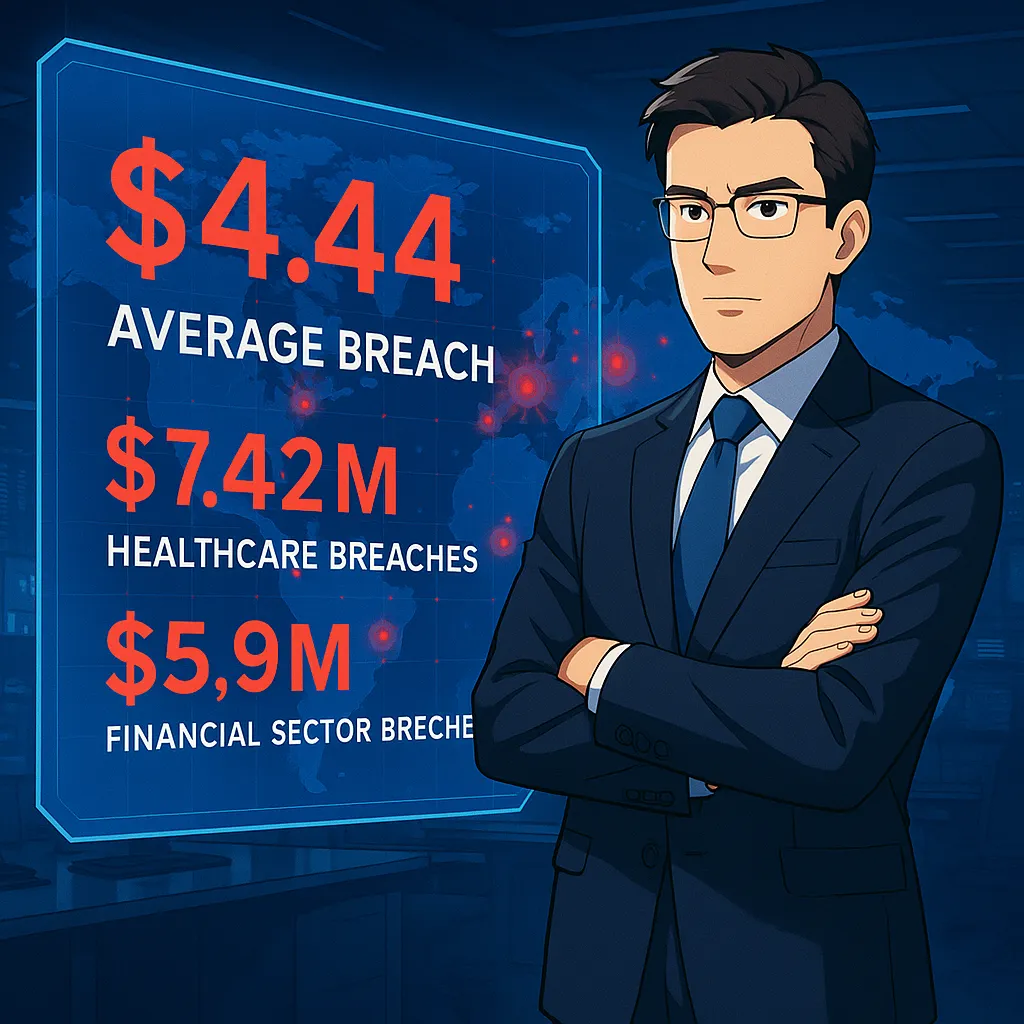
Pirates vs. Ninjas
The average data breach in 2025 costs organizations $4.44 million globally. But that's just the average. Healthcare organizations face $7.42 million per breach, while financial institutions pay $5.56 million .
Incident Response · Governance & Compliance · Threat Intelligence
 Detection & Monitoring
How to Automate OT Security
Automate OT security for enhanced protection & efficiency, streamlining cybersecurity across your industrial systems. Learn more here.
Governance & Compliance
 OT & ICS
The Human Factor in OT Defense
Learn why inexperienced IT staff cannot protect industrial systems, & how to ensure robust cybersecurity with trained professionals. Learn more here.
Detection & Monitoring · Ransomware
 Detection & Monitoring
Beyond Vulnerability Scanning
While penetration testing finds vulnerabilities, OT red team assessments test whether your people, processes, and technology can actually detect and stop a real-world attack.
Incident Response · Ransomware · Governance & Compliance · Threat Intelligence
 Detection & Monitoring
Red Team Assessment vs. Penetration Testing
Pirates charge in loud, finding every crack in your defenses. Ninjas slip through shadows, testing whether you'll even notice. Penetration testing identifies vulnerabilities. Red team assessments test detection.
Incident Response · Threat Intelligence
 Detection & Monitoring
What Is a Cyber Fusion Center?
Traditional SOCs chase alerts while attackers move laterally undetected. When fragmented security operations failed against sophisticated threats, one truth emerged: silos couldn't defend modern networks.
Incident Response · Governance & Compliance · Threat Intelligence
 Detection & Monitoring
The Hidden Threat to Critical Infrastructure
Just ten phishing emails separate cybercriminals from your power grid. When Asahi's bottling lines halted and United Natural Foods froze operations, one truth emerged: trust became the vulnerability attackers weaponize.
Ransomware · Phishing & Email
 OT & ICS
Phishing in OT? Yes, It's Happening. 🏭
They don't need to hack your PLCs anymore—they just need one engineer with remote access to click the wrong link. In 41% of OT incidents, phishing is the entry point.
Detection & Monitoring · Incident Response · Ransomware · Phishing & Email
 Detection & Monitoring
Cybersecurity for Critical Infrastructure
In a world where cyberattacks take 280 days to contain, critical infrastructure became ground zero. When Colonial Pipeline paid $4.
Ransomware
 Detection & Monitoring
If You Don't Know What You Have, You Can't Defend It
Every breach investigation reveals the same smoking gun: a "surprise" asset nobody knew existed.
 Detection & Monitoring
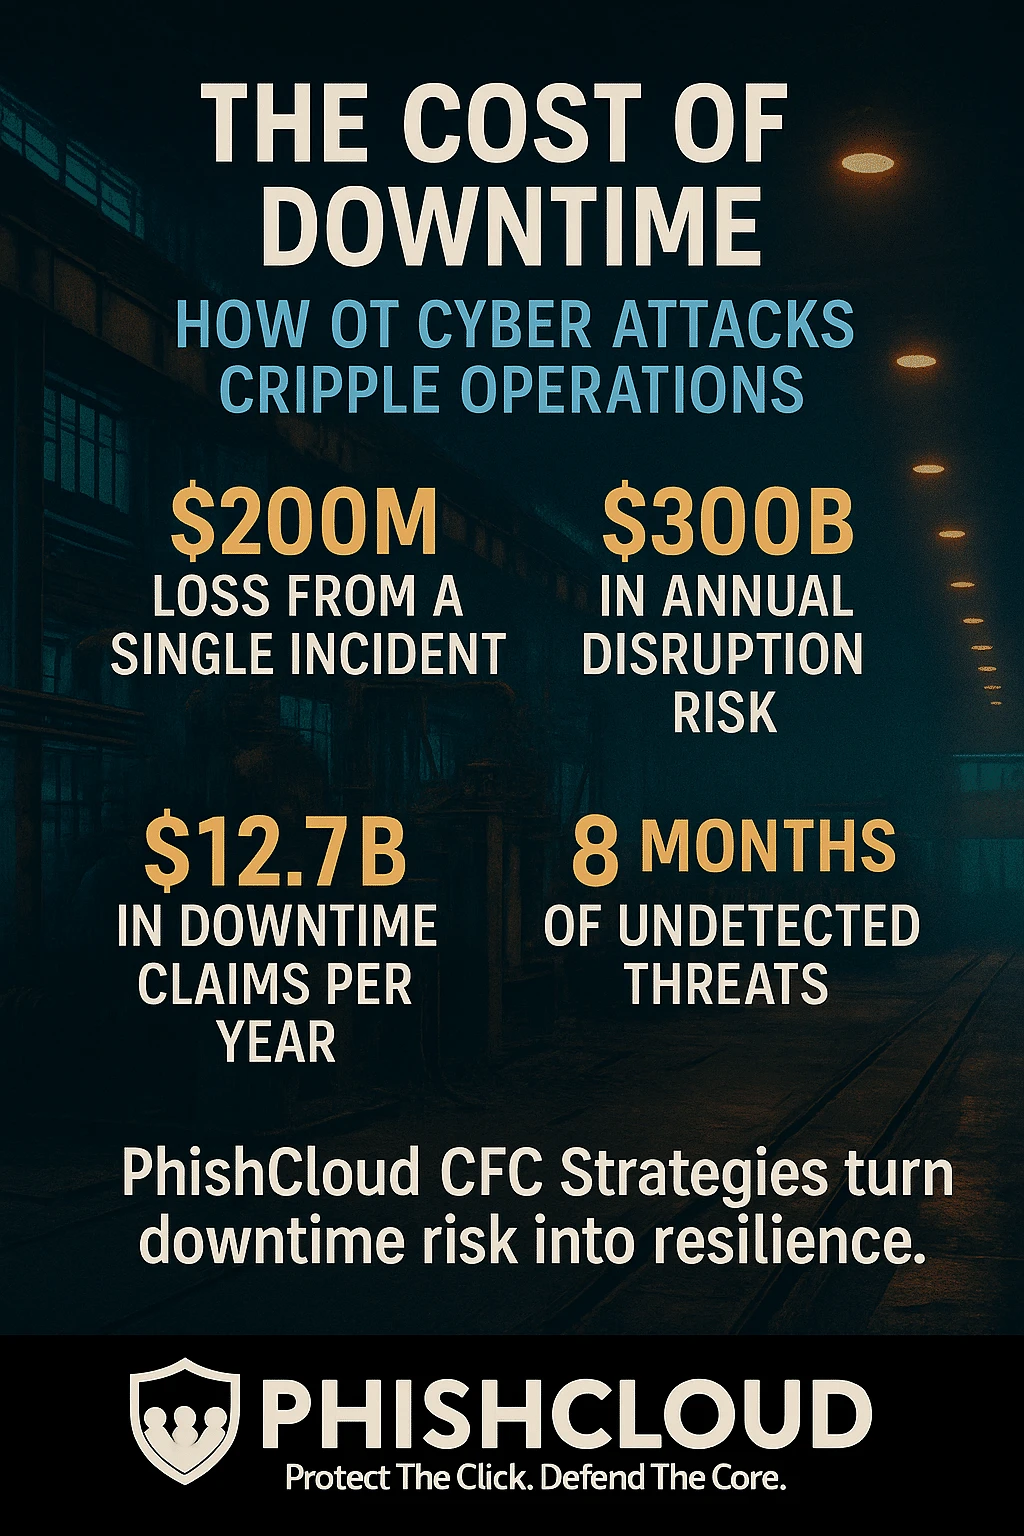
The Cost of Downtime
Learn how OT cyber attacks cripple operations & how to prevent costly disruptions with effective defense strategies. Learn more here.
Incident Response · Ransomware · Governance & Compliance
 Detection & Monitoring
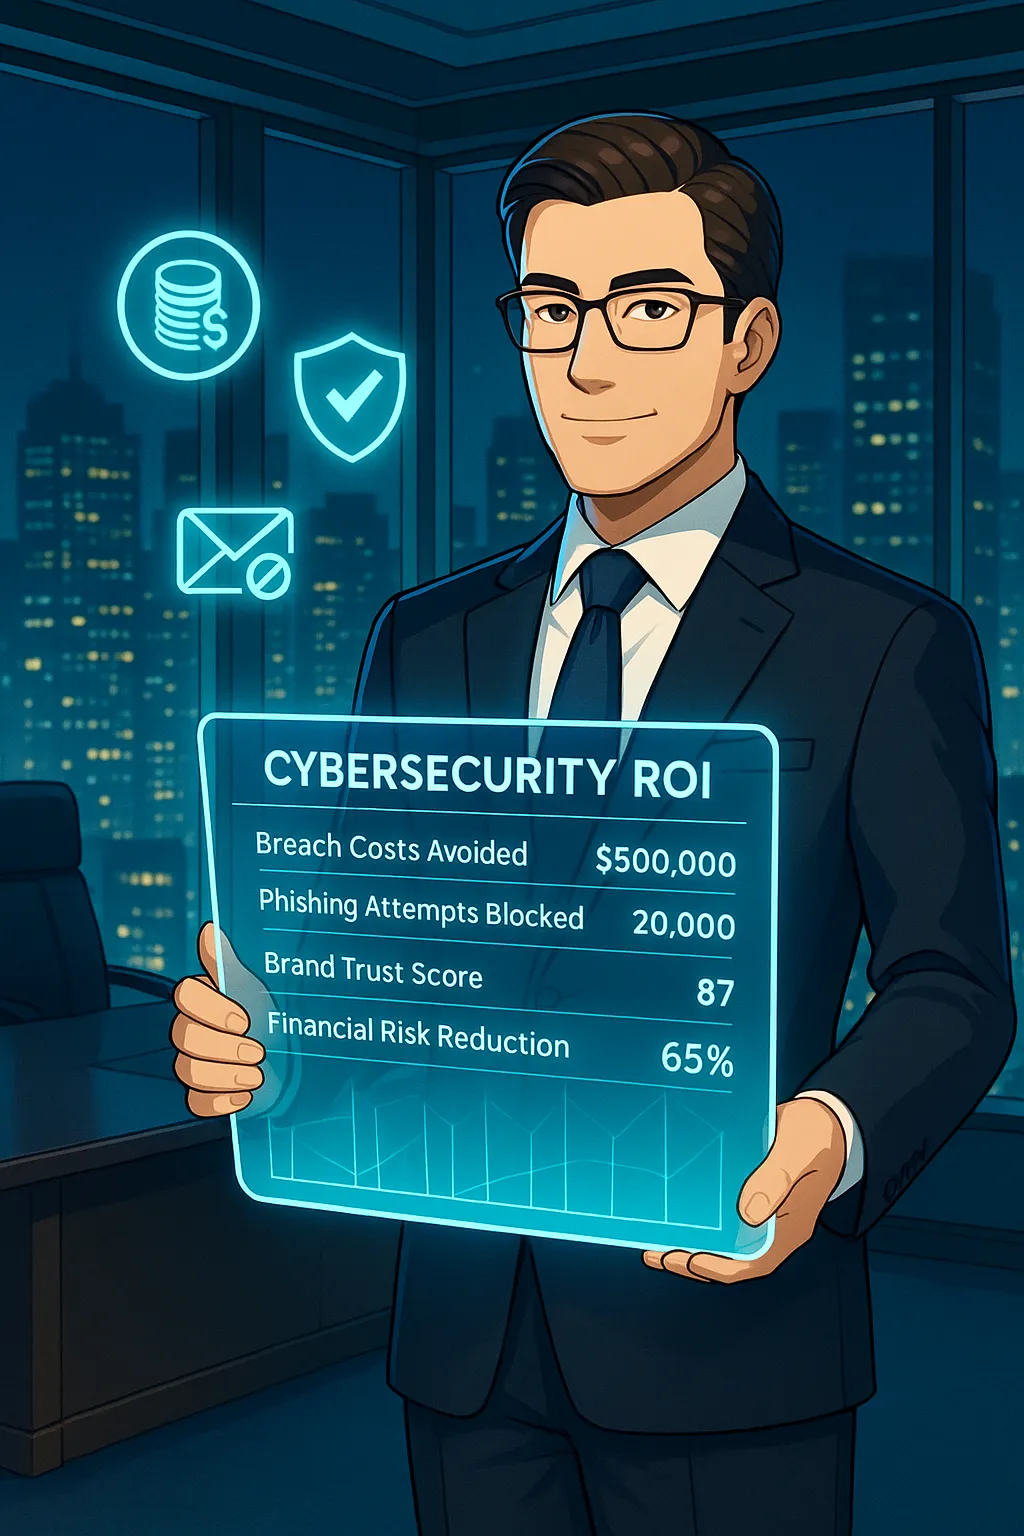
The ROI of Anti-Phishing Solutions
Billions drained. Trust shattered. Reputations destroyed. Phishing breaches don't just steal credentials—they cost millions in recovery, regulatory fines, and brand damage that lasts years.
Incident Response · Phishing & Email · Governance & Compliance
 OT & ICS
Fake Employees, Real OT Risks
June 2025 exposed a chilling truth: North Korean operatives infiltrated 100+ U.S. companies using stolen identities, AI deepfakes, and laptop farms.
Detection & Monitoring
 Detection & Monitoring
Why Traditional OT Security Tools Fail Against Modern Threats
In a world where 78% of OT ransomware attacks start in IT networks, industrial systems became ground zero for a new kind of warfare.
Incident Response · Governance & Compliance
 Detection & Monitoring
The Breach No One Saw Coming 🚰
Thanksgiving weekend. A quiet phone call. Then Robert Bible learned his small Pennsylvania water plant was under attack by Iranian-backed hackers—and he wasn't alone. Five utilities breached.
Incident Response · Governance & Compliance
 Detection & Monitoring
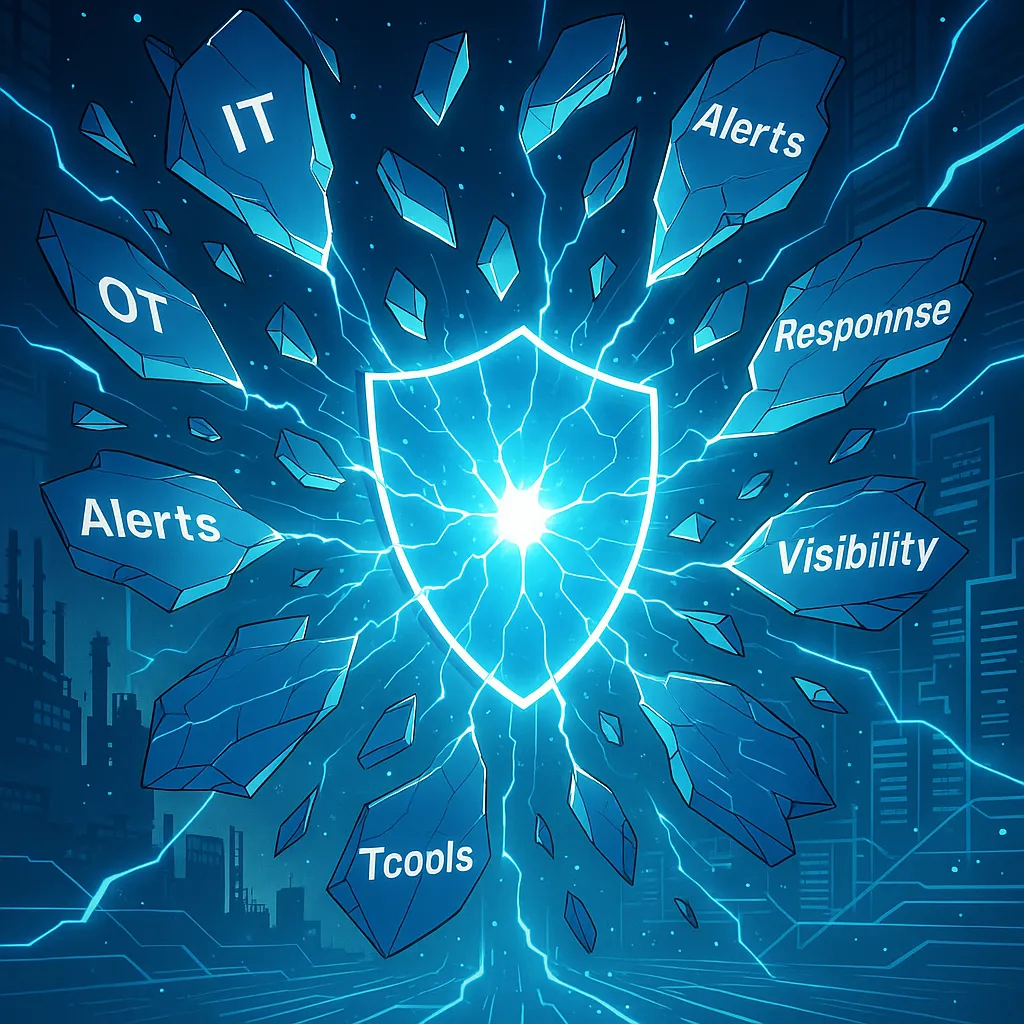
From Fragmented Defense to Unified Resilience 🔗
For decades, IT and OT security lived in separate worlds. Different languages, dangerous 300-day delays, compliance burdens, and disjointed responses left blind spots where attackers thrived.
Governance & Compliance
 Detection & Monitoring
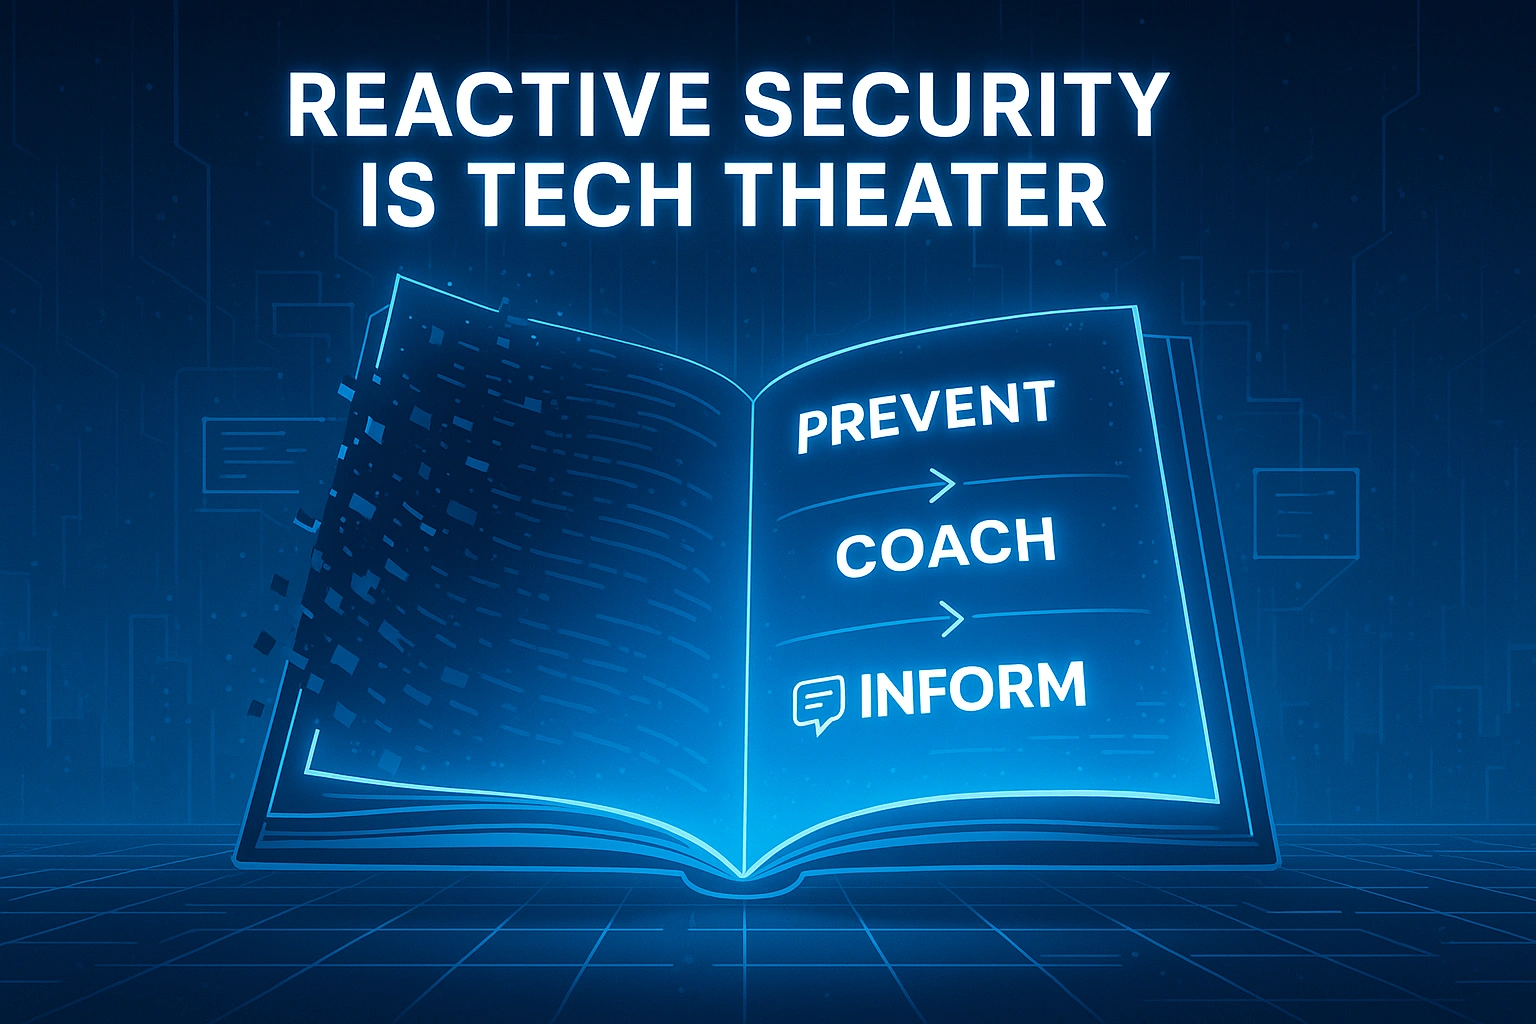
Reactive Security Is Tech Theater: Here's the Real Way to Stop Breaches
In a world where AI attackers craft perfect lures in seconds and threats mutate every few minutes, detection-based systems became ground zero for breach documentation, not prevention.
Incident Response · Phishing & Email
 Detection & Monitoring
Drowning in Data, Starving for Insight
Six monitors, three dashboards, mountains of alerts—and the breach still happens.
Incident Response · Phishing & Email
 Detection & Monitoring
The Click Curve
91% of cyberattacks start with phishing—yet the worst offenders aren't who you'd expect.
Phishing & Email · Risk & Leadership
 Detection & Monitoring
When One Click Kills: Fixing the Human Achilles Heel of Cyber Defense
Achilles fell to a single arrow. Your enterprise falls to a single click. Phishing surged 1,265% as AI weaponized deception, turning employees into unwitting saboteurs.
Phishing & Email
 Detection & Monitoring
Cybercrime Is Exploding: Phishing Is the Engine Behind $9 Trillion in Losses
Eight hundred sixty billion dollars. That's what cybercrime cost the world in 2018. Six years later: $9.22 trillion—a tenfold explosion with no brakes in sight. Phishing isn't just part of this crisis; it's the engine.
Phishing & Email
 Detection & Monitoring
Securing the Click: Why Endpoint Phishing Protection is Non-Negotiable
In a world where 2.6 billion phishing interactions bypassed email gateways, enterprise defenses became ground zero for a new battlefront.
Phishing & Email
 Phishing & Email
Beyond Red and Green 🚦
Traffic lights without yellow meant chaos at intersections, drivers blindsided at every turn.
 Detection & Monitoring
The Blind Spot in Cybersecurity
3.4 billion phishing emails sent daily—yet organizations can't answer three critical questions: Who clicked? What did they engage with? What damage occurred?
Incident Response · Phishing & Email
 Incident Response
When Humans Become the Hack 🎯
Your firewalls are bulletproof. Your endpoints are hardened. Your networks are segmented. So why do 95% of breaches still trace back to your people?
Phishing & Email · Governance & Compliance
 Detection & Monitoring
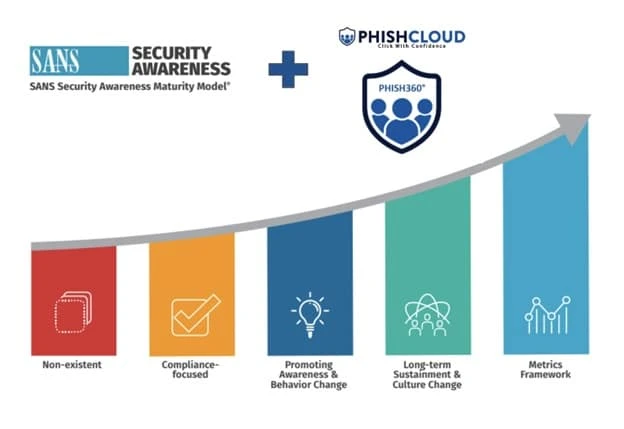
How Mithryl Systems PHISH360° Accelerates the SANS Security Awareness Maturity Model
Accelerate your security awareness maturity model with Phish360 to improve your organization's defenses & training efficiency. Learn more here.
Incident Response · Phishing & Email · Governance & Compliance
 Detection & Monitoring
Cybersecurity GPS: Your Guide Through Phishing Hazards
In a world where London cabbies memorized 25,000 streets to navigate the city, expertise wasn't enough when roadblocks appeared.
Phishing & Email
 Governance & Compliance
The Real 1%: A Lesson from My Father
In a world where 700 million users interact with technology, only 70 million can code—and within that elite 10%, a mere 700,000 truly understand the system's backbone.
 Detection & Monitoring
From Click to Crisis: How Phishing Powers Ransomware, Spyware & Data Theft
In a world where 29 billion cybersecurity events revealed 2.6 billion phishing interactions, organizations became ground zero for ransomware, spyware, and credential theft.
Incident Response · Ransomware · Phishing & Email
 Detection & Monitoring
Unwrap the Truth
Link-wrapping promised security—but delivered encoded jumbles that hide destinations from users.
Phishing & Email
 Detection & Monitoring
The Phishing Paradox: Training Doesn't Work, and Tools Aren't Enough
Training reached 99% of organizations. Phishing breached 84%. The paradox: neither tools nor training alone stops modern attacks. Half of malicious emails bypass SEGs. Thirty percent click despite training fatigue.
Incident Response · Phishing & Email
 Detection & Monitoring
Don't Be Blockbustered
Cyberattacks take weeks to detect while we get instant spellcheck alerts—priorities completely out of whack.
Phishing & Email
 Detection & Monitoring
Stagnation Fuels Breaches ⚠️
Ninety percent of breaches start with a single click—yet defenders are armed with twenty-year-old tactics.
Incident Response · Phishing & Email · Governance & Compliance
 Detection & Monitoring
Beyond the Inbox: The Phishing Threat You're Ignoring
Phishing emails spiked 28% while 52.2% bypassed traditional defenses—but email was just the beginning.
Phishing & Email
 Detection & Monitoring
Don't Strike Out on Cyber Threats ⚾
Reggie Jackson could call the pitch before the ball left the pitcher's hand—70% accuracy by reading subtle cues. In cybersecurity, we're still waiting for the ball to cross the plate before we swing.
Phishing & Email
 Ransomware
Are You a Technical CISO or a Compliance CISO?
Two roads lead to the CISO chair: the trenches of red teams and pentesting, or the corridors of governance and compliance. Hundreds of conversations reveal a pattern.
Governance & Compliance
 Incident Response
Box-Checking Won't Save You
Compliance became the zone defense no one questioned—until attackers walked right past it.
Phishing & Email · Governance & Compliance
 Detection & Monitoring
Awareness Is Step One—Continuous Protection Stops Attacks
1.5 million phishing incidents in 90 days exposed a brutal truth: cybersecurity became ground zero for a crisis that training alone can't stop.
Incident Response · Ransomware · Phishing & Email
 Phishing & Email
Fake Attacks, Real Blind Spots
Productivity losses from phishing already cost $1.8 million annually, yet 61% of employees who fail simulations show no improvement on follow-up tests.
Governance & Compliance
 Detection & Monitoring
Alert Fatigue Is a Business Model — Not a Bug
They perfected the art of selling security—then abandoned the innovation. Big cyber floods your SOC with thousands of alerts they know cause fatigue. They slap "AI" on decade-old tools and call it progress.
Phishing & Email · Governance & Compliance
 Phishing & Email
Protecting Critical Infrastructure
In a world where cybercrime costs $9.5 trillion annually, critical infrastructure became ground zero for industrial warfare.
 Detection & Monitoring
Living on the Edge of Cyber Chaos 🎭
Cybersecurity Awareness Month wraps up, but cybercriminals don't take holidays.
Incident Response · Ransomware · Phishing & Email
 Detection & Monitoring
Beyond the Basics: How Phishing Continues to Infiltrate Systems
In a world where phishing evolved beyond email into social media, SMS, and third-party apps, organizations became ground zero for sophisticated infiltration.
Phishing & Email
 Detection & Monitoring
The Evolution of Cyber Threats 🦷🔪
Phishing evolved from simple bait into sophisticated predators targeting even cybersecurity vendors. Any.Run, a leading malware sandbox, fell victim to fake Microsoft login pages—breach undetected for a month.
Incident Response · Phishing & Email
 Phishing & Email
Only Phools Phall Phor Phishing
Think of some of the greatest teams in history.
 Phishing & Email
Houdini and Cybersecurity 🎩✨
Houdini's death-defying escapes weren't luck or spontaneity. Every lock pick, every knot, every move was rehearsed meticulously.
The Battle of Trafalgar (1805)
Admiral Nelson crushed Napoleon's fleet in 1805 by breaking tradition, trusting his captains, and using tactics over brute force. Modern cybersecurity faces the same challenge. Parallel defenses fail.
 Phishing & Email
Are Phishing Simulations Like Real Phishing Attacks?
Every October, CISOs roll out phishing simulations—corporate batting practice against yesterday's threats.
 Incident Response
Swing, Slice, Patch, Repeat: The Endless Grind of Cyber Defense
Golf and cybersecurity share the same brutal truth: both humble you, both never end, and both punish overconfidence. New $2,000 drivers still slice into the woods. New security tools still get bypassed by phishing.
 Phishing & Email
Cloud, DMs, and Teams: Hackers Moved, Your Security Didn't
Email attacks plummeted from 92% to 64%, yet businesses still pour millions into secure email gateways like it's 2018.
 Incident Response
Cybersecurity Needs Its Chuck Yeager Moment
Chuck Yeager shattered the sound barrier in 1947. Seventy-eight years later, cybersecurity companies still peddle the same password advice from the 1990s.
Phishing & Email
 Detection & Monitoring
The Invasion of the TOADs 🐸☎️
Ten million TOAD messages flood inboxes monthly, bypassing email filters by replacing links with phone numbers. Victims call, trust the voice, download "support tools," and grant full device access.
Phishing & Email
 Phishing & Email
109 Seconds to Disaster: The High-Speed Threat of Phishing Attacks
The clock starts the moment your employee sees the email. 60 seconds to engage. 21 seconds to click. 28 seconds to expose everything.
 Incident Response
Digital Security is Physical Security in Disguise
Hackers don't need a crowbar to break into your life. They just need a weak password, an ignored update, or one careless click.
Phishing & Email
 Incident Response
Usain vs. The Snail: Why Cybersecurity Can't Keep Up
Technology races forward at warp speed while cybersecurity crawls behind like a snail chasing Usain Bolt. This gap is the vulnerability hackers exploit daily.
Phishing & Email
CyberSecurity Paradox
Solomon warned that nothing is new under the sun—yet every security breakthrough sharpens the adversary's blade. AI defends; AI deceives. Speed saves us; speed blinds us.
 Detection & Monitoring
The Myth of Cybersecurity Awareness
Bruce Lee mastered martial arts through decades of practice. Watching his films won't save you from a mugger. Cybersecurity awareness works the same way—knowing phishing exists doesn't mean you can stop it.
Phishing & Email
The Irony of Invention
Technology's promise was simple: make life easier.
 Phishing & Email
Wolves in Sheep's Clothing
For every 10 acts of digital kindness, one wolf waits to exploit it.
 Phishing & Email
Saddle Up for Safety! 🤠
The Wild West of the internet stretches far beyond email—criminals stalk you on social media, search engines, and every corner of the web.
 Detection & Monitoring
Blunders Through Time: How History Warns Us About Cybersecurity
The Trojans wheeled in a giant wooden horse and called it a gift. Kyle from accounting downloaded malware because a prince needed his help. Same energy, different millennium.
Phishing & Email
 Detection & Monitoring
You Shall Not Phish: Outsmarting the Gandalfs of Cybercrime
"You shall not pass... without giving up your personal info!" Tech-savvy Gandalfs lurk in every inbox, chat, and social feed, casting spear phishing spells and laying scam traps across your digital kingdom.
Phishing & Email